Controls per system
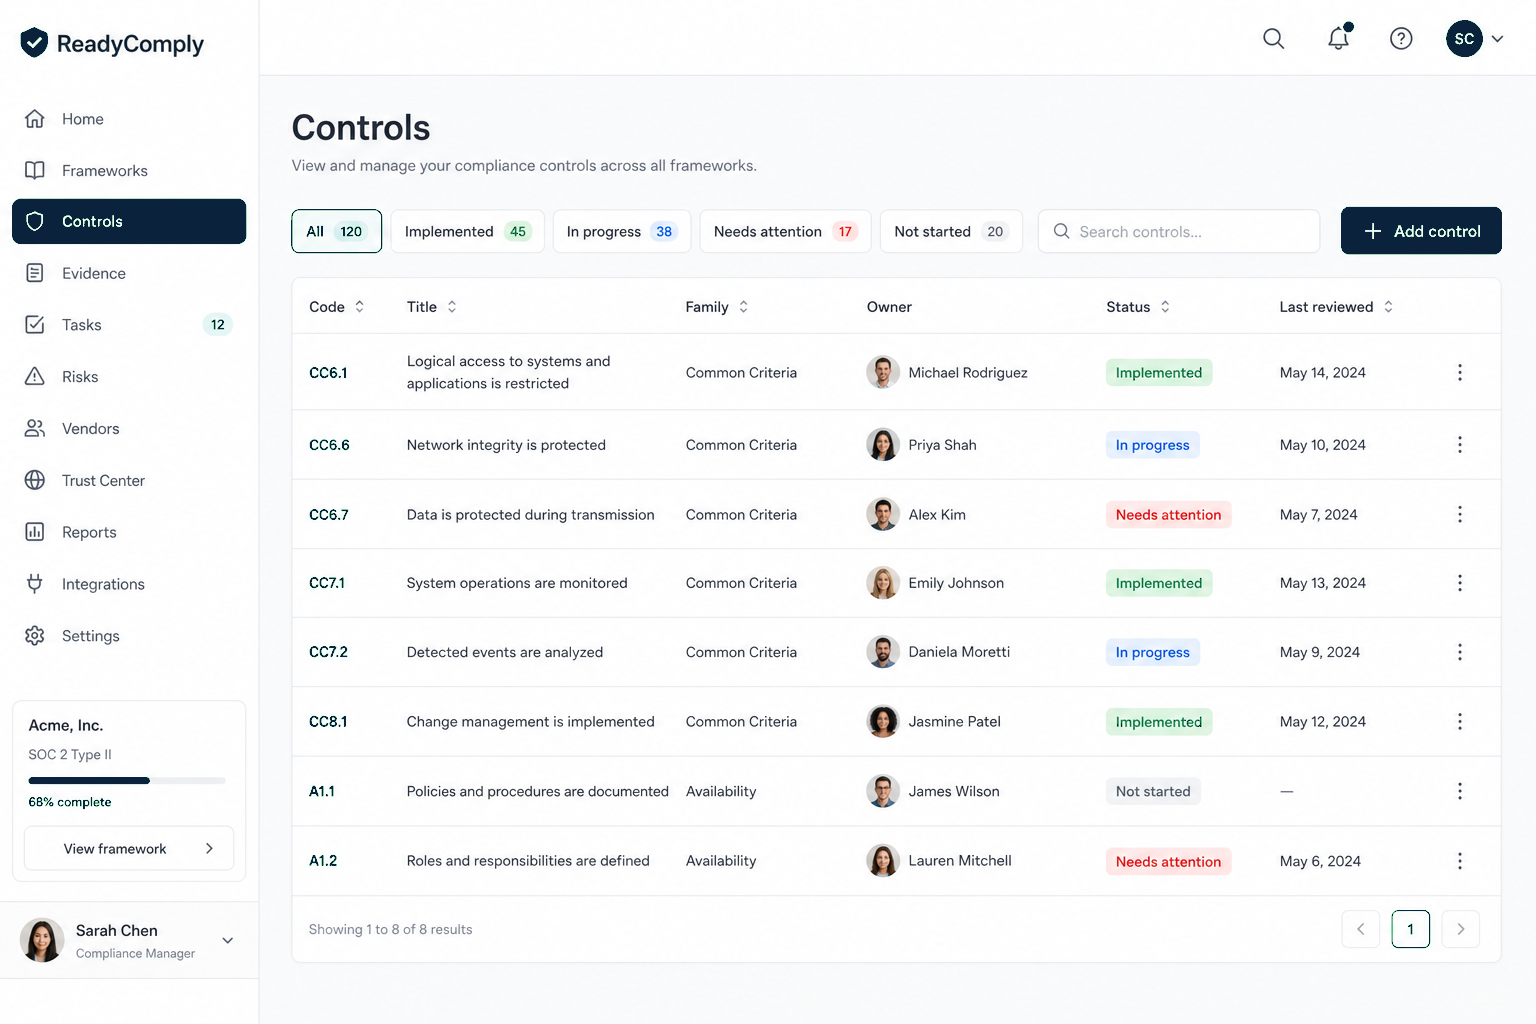
Not a shared spreadsheet with last year’s owner still in the cell.
Solutions · Startups
You do not have a GRC team. You have a product, a cloud account, and a buyer who asked for SOC 2. ReadyComply is the register for that first cycle — not a certificate you purchase.
Who this is for
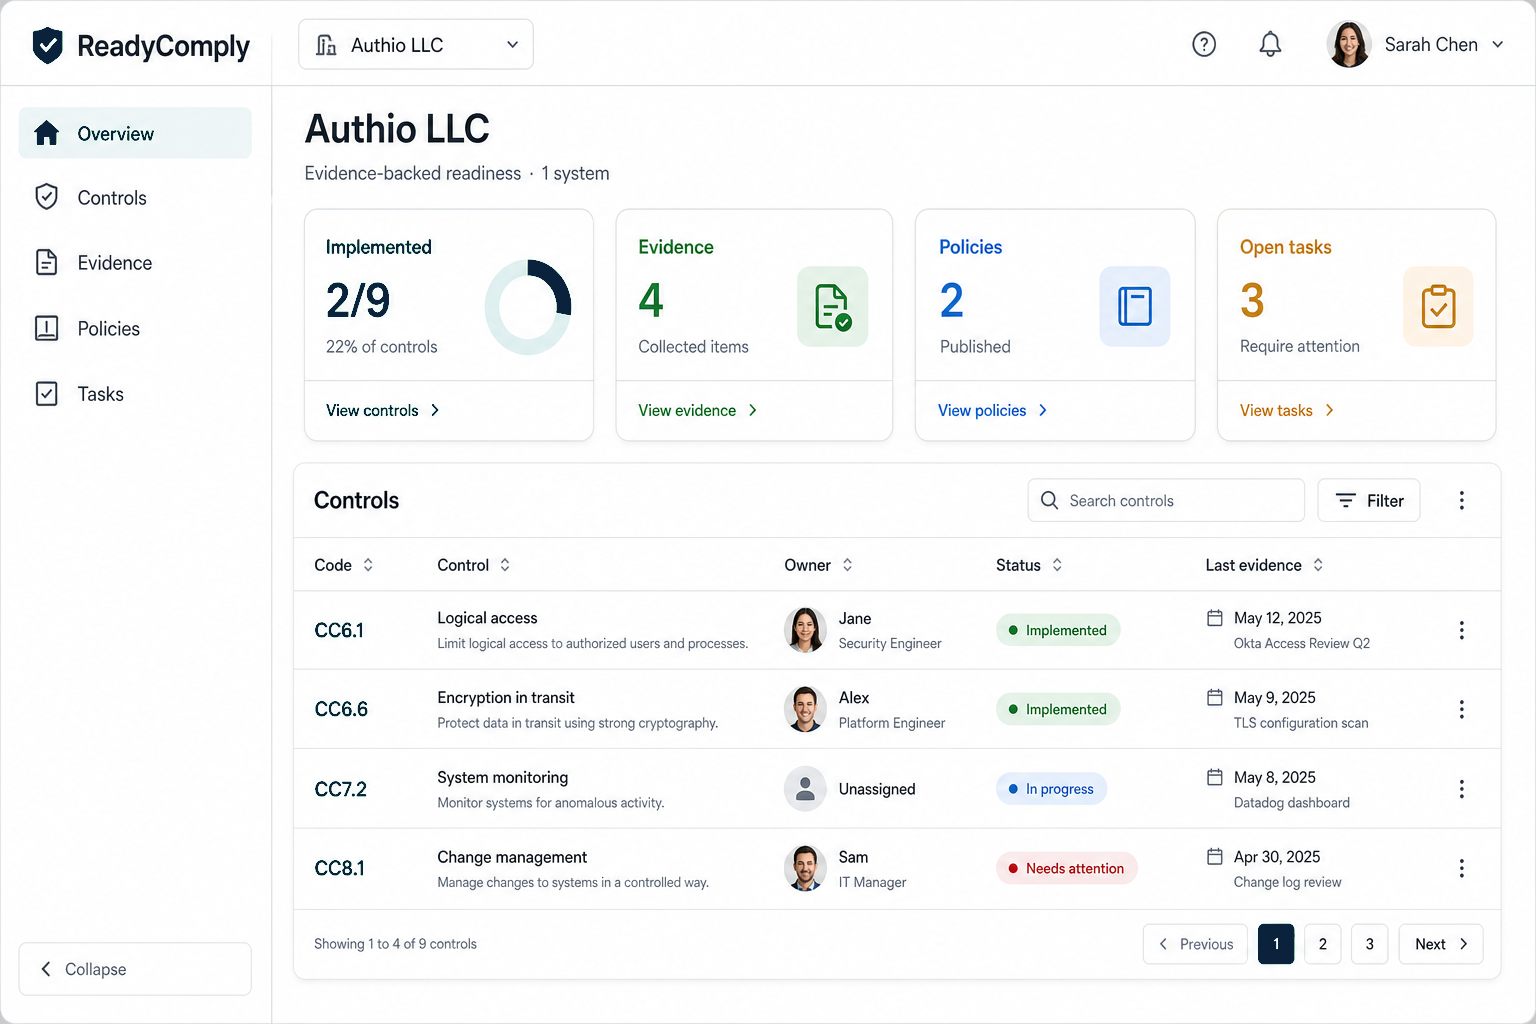
Name the entity. Name the product. Instantiate Security. File what you already have. Open tasks for what you do not. That is the whole first pass. Platforms that skip this and sell a badge are selling someone else’s opinion.
The first pass
If you cannot draw the boundary, you are not ready for a firm.
On a five-person team the owner is often you. Write that down.
Honesty here is cheaper than a finding in the period.
Connectors come later. The loop has to work without them.
ReadyComply is not the firm, does not pick one, and does not issue the report.
What you get
Not a shared spreadsheet with last year’s owner still in the cell.
The export you already ran, filed against the control it supports.
What you claim you do, next to the criterion it maps to.
Gaps are work. Work has an owner.
Also in ReadyComply
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Sign in. If you are in the portfolio, you already have an organization.
Sign in