Resources · SOC 2 checklist
The loop, in order. Mapped to the workspace.
This is a readiness checklist, not a certification. Checking a box here does not mean you have a SOC 2. It means the register has the thing an examiner will ask for.
Scope
Before you instantiate a single control.
- 01
Legal entity is named.
The report is issued to a company, not a product nickname.
- 02
System boundary is written down.
Apps, infra, and vendors in scope. ReadyComply stores this as systems on the org.
- 03
Trust Services Criteria you will claim are chosen.
Security is the starter set. Do not add availability or privacy unless you will evidence them.
Register
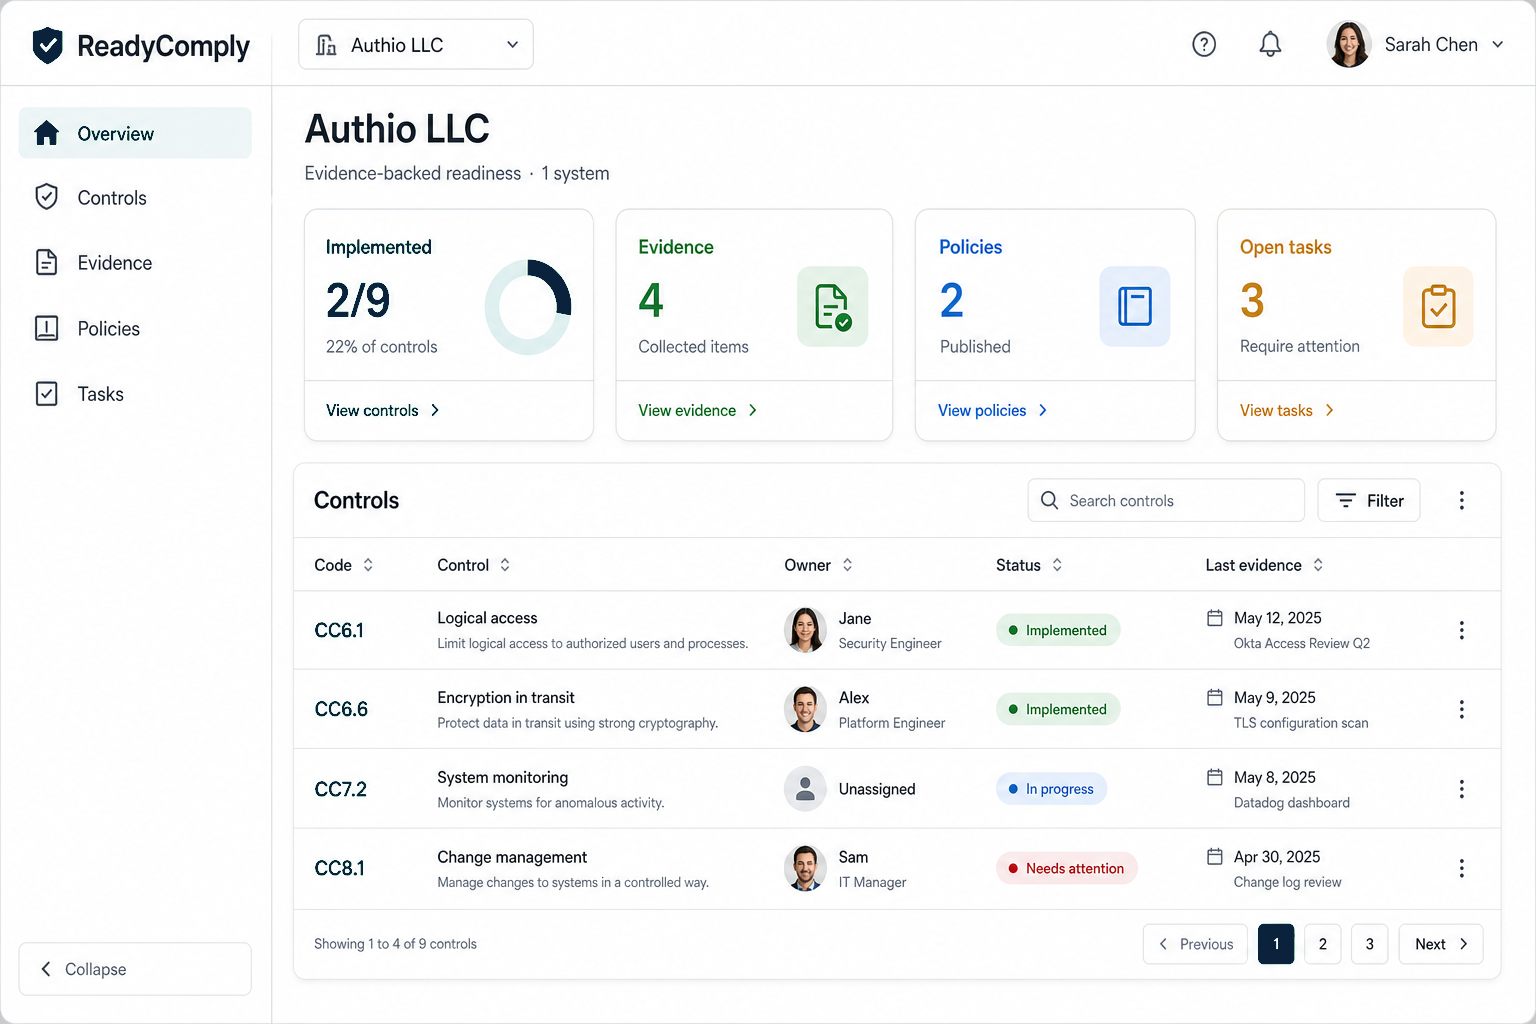
Inside ReadyComply.
- 01
Starter Security family instantiated per system.
Each criterion has an owner and a status a human set.
- 02
Implementation statements written.
How the control operates here — not a paste of the AICPA language.
- 03
Not applicable has a rationale.
Empty is not a reason. The field exists so you fill it.
- 04
Evidence filed against the controls you call implemented.
Type, source, collected-at, optional hash. See Evidence.
- 05
Policies drafted and versioned.
Current text is knowable. See Policies.
- 06
Gaps are tasks with owners and due dates.
See Remediation. Closing the task does not erase the trail.
Firm
When you are ready for a CPA.
- 01
You hired a licensed firm. ReadyComply did not.
We do not broker audits and do not issue the report.
- 02
The period (Type II) or date (Type I) is chosen with that firm.
The register has to stay current through that window.
- 03
The trail can explain how a control got to implemented.
See Audit trail.
Workspace pages
Each line above has a product page.
Controls · Evidence · Policies · Remediation · Audit trail
Also in ReadyComply
Open the modules.
Controls
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
Evidence
File what you have against a control. Manual upload or a read-only connector.
Policies
Versioned drafts next to the controls they support. Know which text is current.
More
Guide, limits, FAQ.
SOC 2 guide
What the work actually is, and what a platform can and cannot do.
ISO 27001 guide
An ISMS you can operate, versus a certificate you can buy.
HIPAA guide
Security Rule readiness for teams that may touch ePHI.
GDPR guide
Accountability in the register, not a privacy badge.
ISO 27001 checklist
Scope, ISMS clauses, Annex A themes, then a certification body.
HIPAA checklist
Safeguards, BAAs, and evaluation — not an OCR stamp.
GDPR checklist
Purposes, RoPA, rights, processors, transfers.
What this is not
ReadyComply is software. It is not an auditor, a report, or an attestation.
FAQ
Straight answers on Authio, scope, and what ships today.
Run the checklist against a real system.
Sign in. If a line is empty in the workspace, that is the next task — not a marketing problem.
Sign in