Resources · ISO 27001 checklist
The ISMS loop, in order. Mapped to the workspace.
Checking a box here does not mean you are ISO 27001 certified. It means the register has the thing a body will ask for.
Scope
Before you treat Annex A as a shopping list.
- 01
ISMS scope is written.
Entity, systems, locations, suppliers. Out of scope has a reason.
- 02
Interested parties are named.
Customers, regulators, personnel, providers — clause 4 is not decoration.
- 03
Information security policy is versioned.
Current text lives in ReadyComply, not a lost Drive file.
ISMS
Clauses 5–10 in the register.
- 01
Leadership and owners are people.
Not a shared inbox. Recorded on the control.
- 02
Risks and treatments are current.
Planning links to tasks. A static heat map is a finding.
- 03
Competence and documents are filed.
Support is evidence, not a claim.
- 04
Internal audit and management review have dates.
Performance evaluation is a control with a next-review field.
- 05
Nonconformities are tasks.
Improvement does not erase the trail.
Annex A
Themes you will actually evidence.
- 01
Organizational, people, physical, technological applied or N/A.
N/A needs a rationale. Inherited physical still needs the provider attestation.
- 02
A certification body is yours to hire.
ReadyComply is not the body and does not print the mark.
- 03
The Statement of Applicability names a reason for every theme.
Applied or excluded, both need a sentence. The SoA is a control-by-control record, not a checkbox export.
- 04
Evidence links back to the clause, not just the Annex A code.
A screenshot with no clause reference is a filing problem for the auditor to solve on your dime.
Also in ReadyComply
Open the modules.
Controls
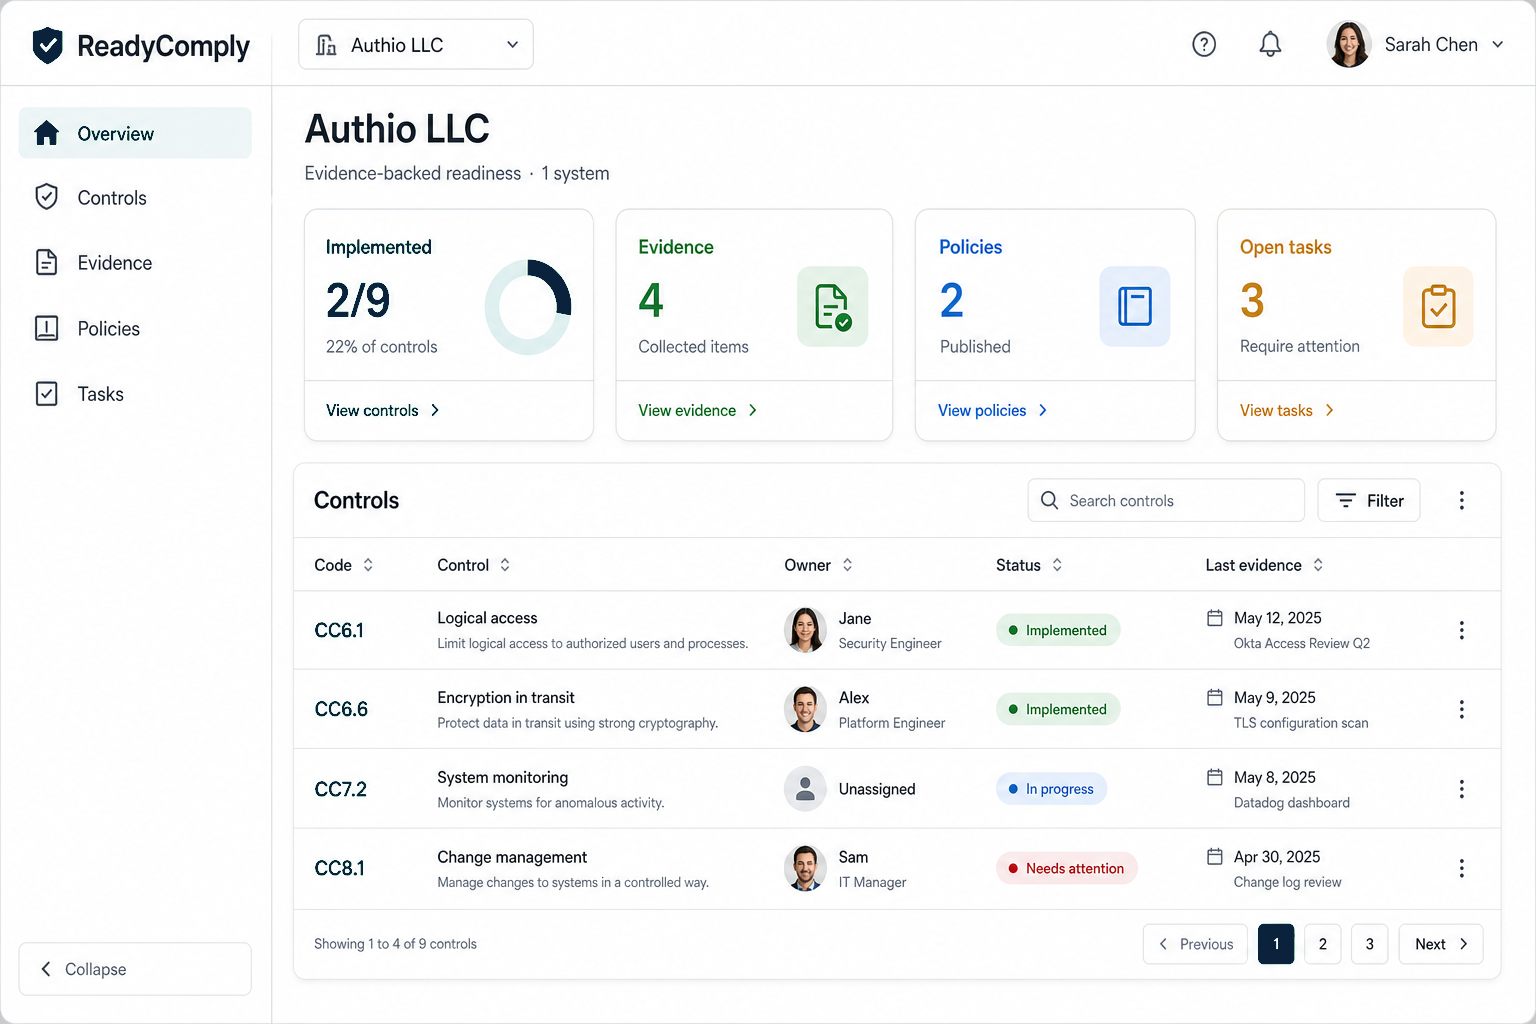
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
Evidence
File what you have against a control. Manual upload or a read-only connector.
Policies
Versioned drafts next to the controls they support. Know which text is current.
Frameworks
All four catalogs.
SOC 2
Trust Services Criteria as a readiness register. The report is still a CPA firm.
ISO 27001
ISMS clauses and Annex A themes. Certification is a body, not this product.
HIPAA
Security Rule safeguard families. A BAA and an OCR review are still yours.
GDPR
Accountability articles for a SaaS register. Not a supervisory-authority opinion.
Guide
Read the longer page.
Open the workspace. Keep the register current.
Sign in. Create the first system. Start with what you can already prove.
Sign in