Scope first
Legal entity, locations, products, and suppliers. Out of scope needs a reason.
Resources · ISO 27001 guide
ISO/IEC 27001 certification is an independent audit against a scoped management system. ReadyComply holds the clauses and Annex A themes. It does not certify you.
The distinction
Certification bodies look for a living system: scope, risk, competence, internal audit, management review, and improvement. A folder of templates with last year’s date is a finding. The register has to stay current through the cycle.
The work
Legal entity, locations, products, and suppliers. Out of scope needs a reason.
You apply themes because the risk treatment says so, not because a vendor dumped 93 rows.
Internal audit and management review are clause 9 and 10, not optional extras.
Stage 1 and stage 2 are theirs. ReadyComply is the file they should not have to hunt.
Where ReadyComply stops
There is no passing grade for an Annex A theme in the product. Status is a human field. Connectors, when they exist, attach evidence to a clause or theme. They do not close a nonconformity, and they do not stand in for the auditor's stage 1 and stage 2 visits. If a page on this site sounds like a mark you can buy, it is wrong.
Framework
Workspace
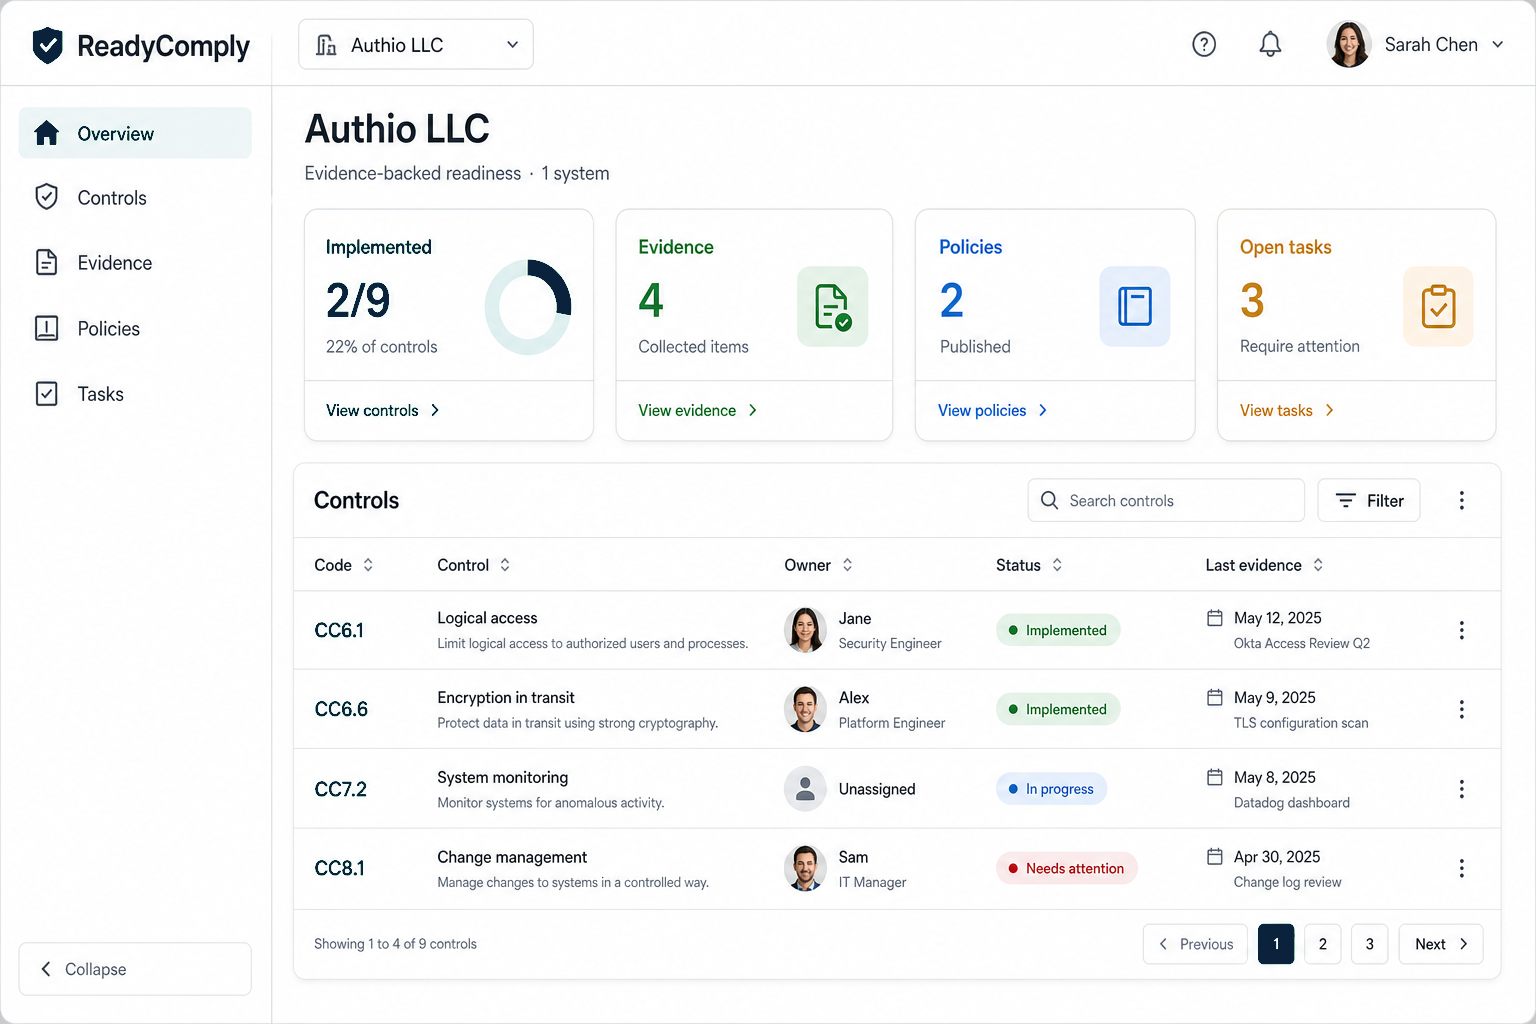
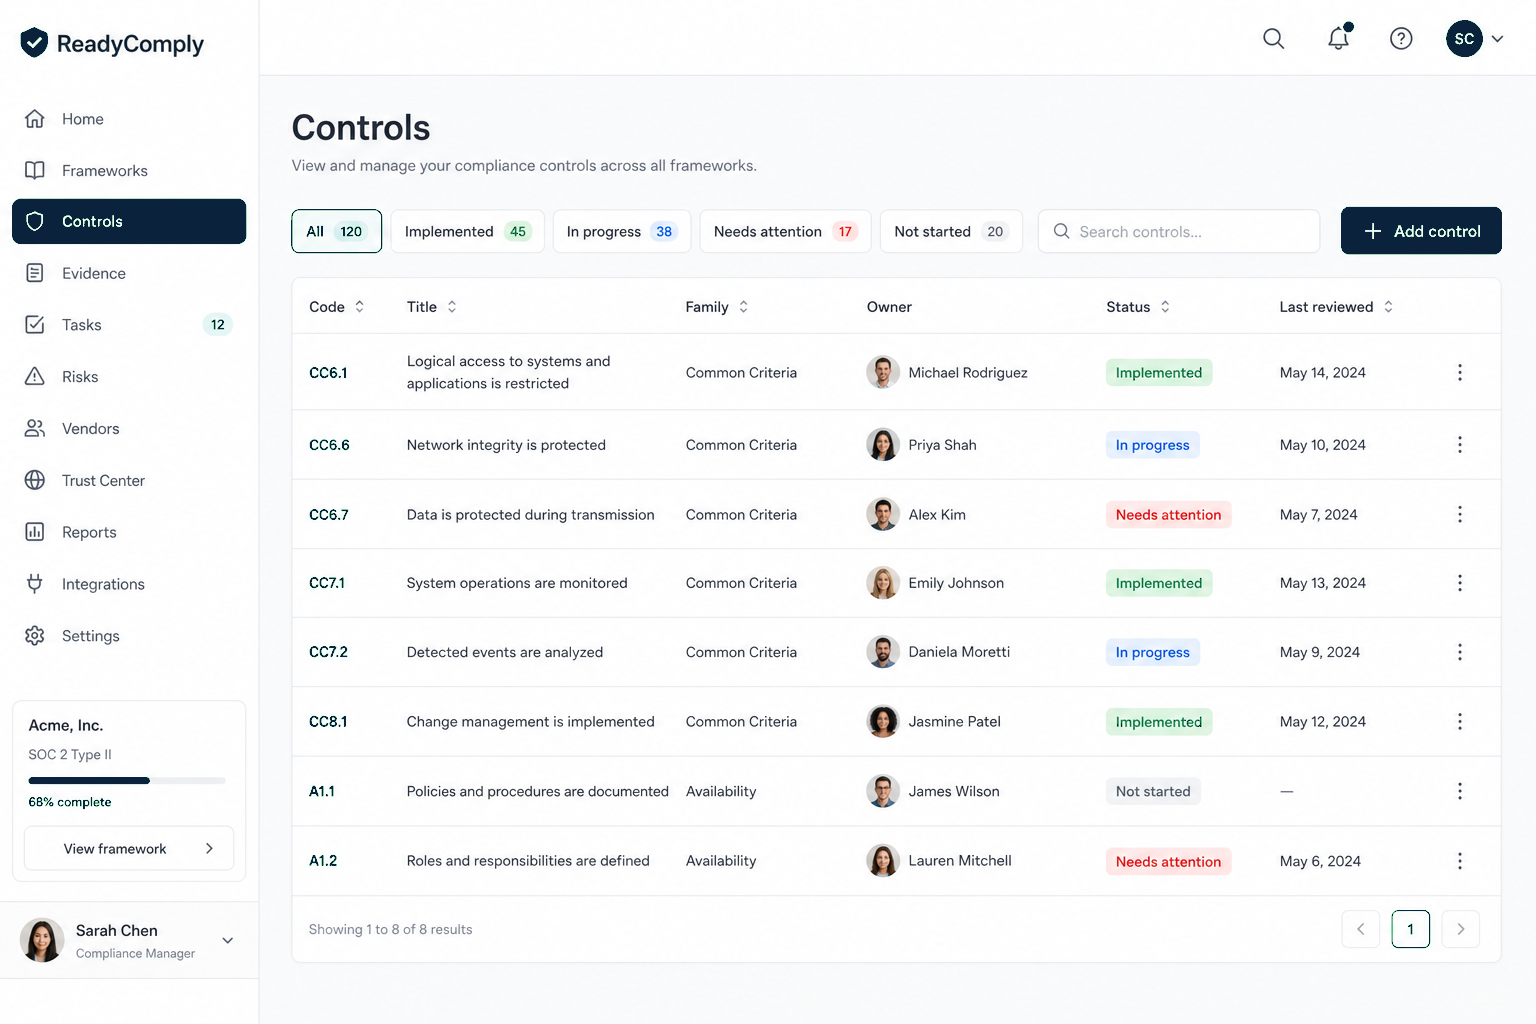
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
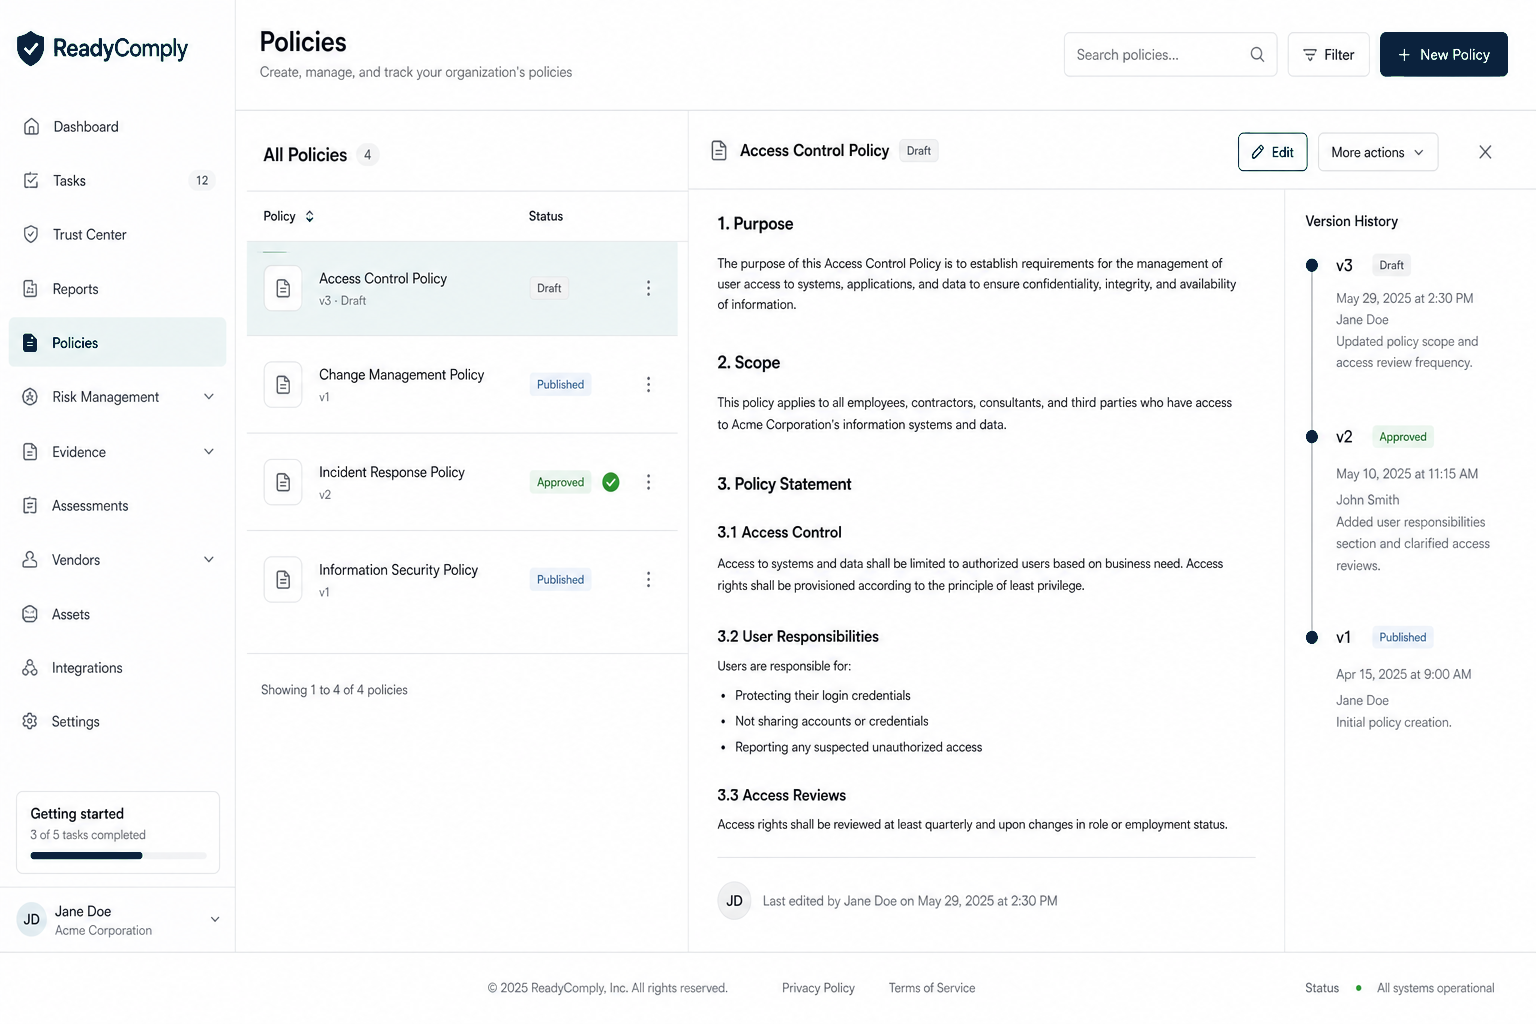
Versioned drafts next to the controls they support. Know which text is current.
Checklist
Sign in. Create the first system. Start with what you can already prove.
Sign in