Classify the data
ePHI is not only a medical record. Auth metadata can be PHI when it is tied to health access.
Resources · HIPAA guide
HIPAA is a US statute and a set of rules. If you are a covered entity or business associate, you implement safeguards around ePHI. ReadyComply holds that register. It does not authorize you and does not sign your BAA.
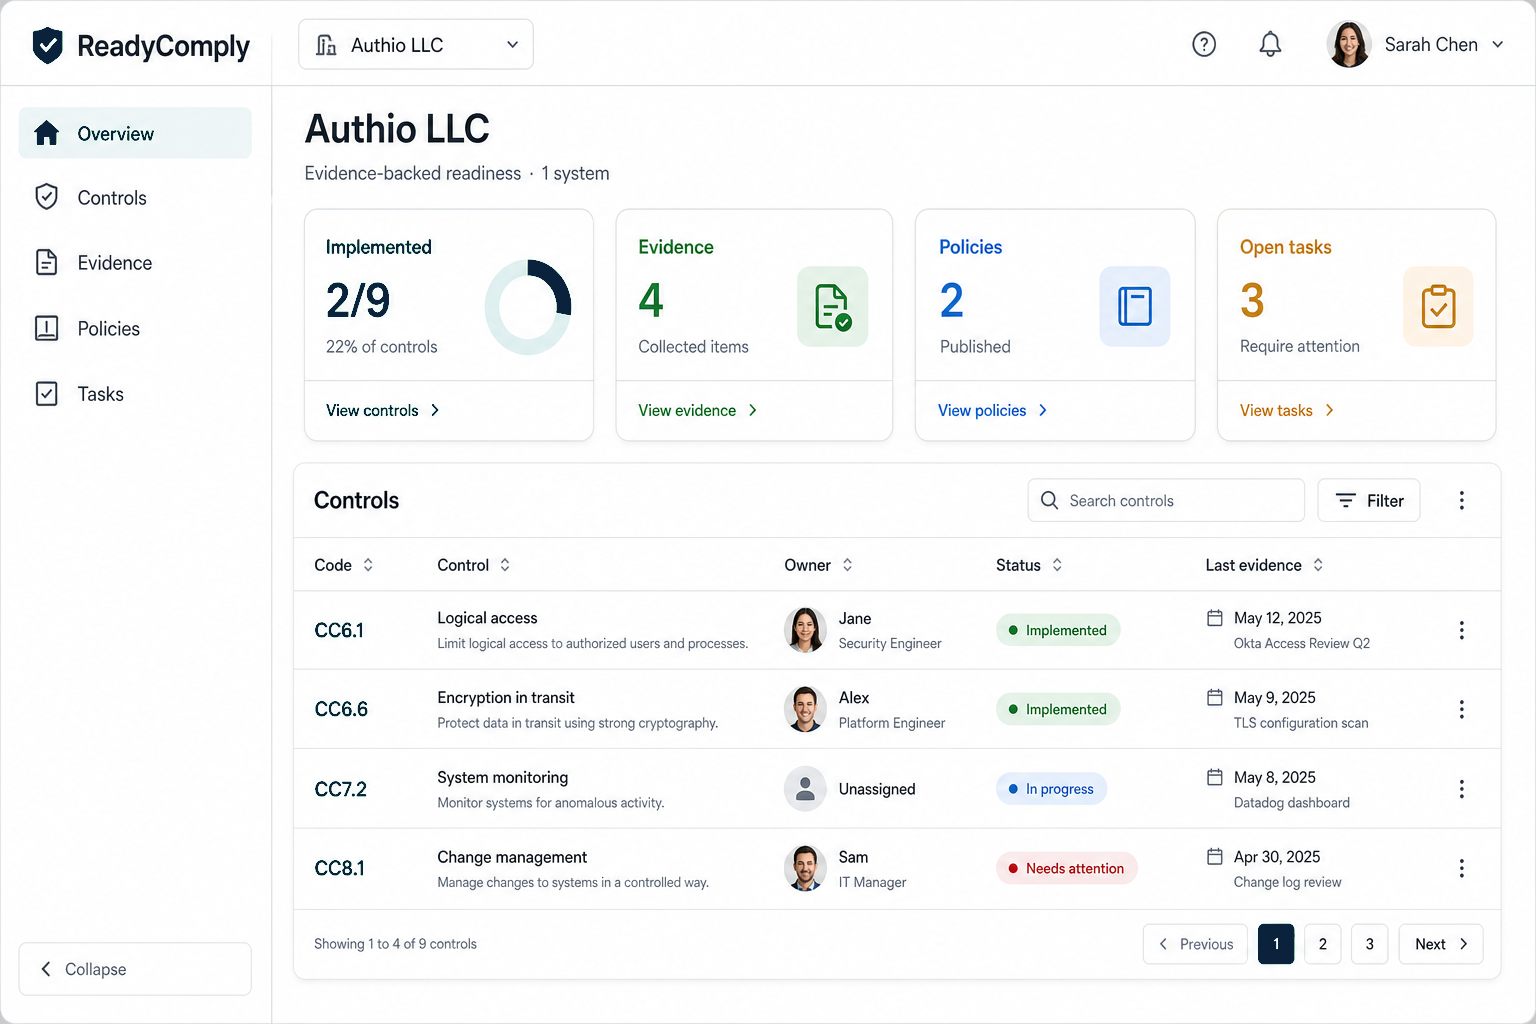
The distinction
Customers will send a BAA. Signing it without a risk analysis, a named official, and technical safeguards is how you inherit someone else’s incident. File the BAA as evidence. Do the safeguards as controls.
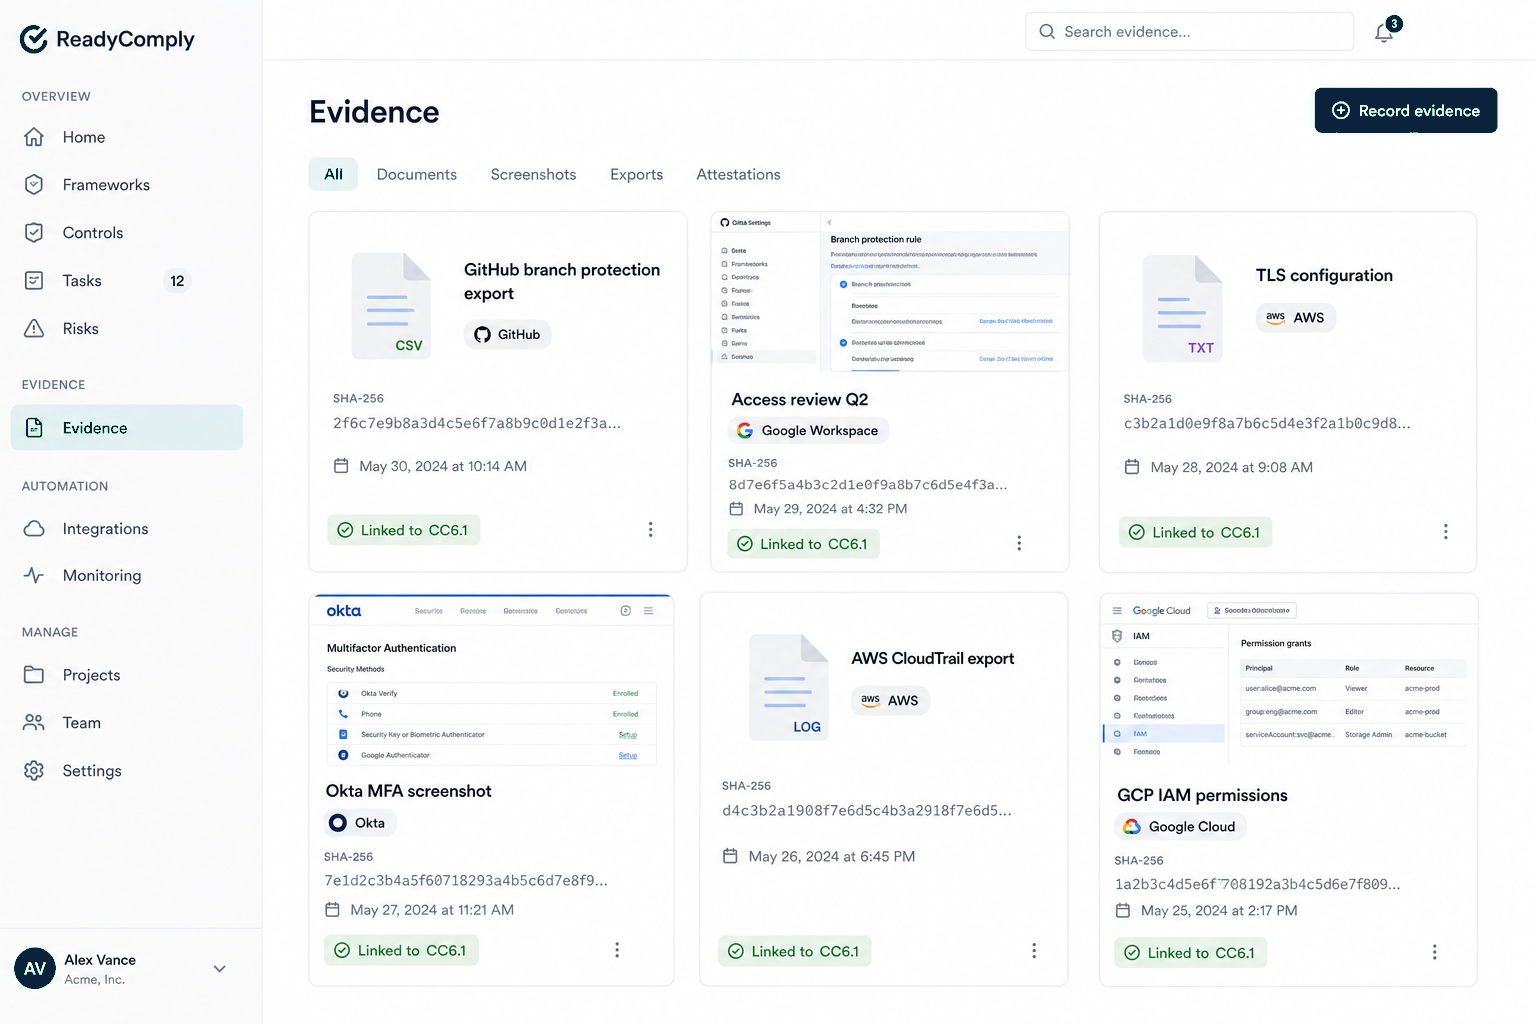
The work
ePHI is not only a medical record. Auth metadata can be PHI when it is tied to health access.
Addressable still needs a documented decision. Empty is not equivalent.
Anyone who creates, receives, maintains, or transmits ePHI for you needs a BAA.
Periodic. Dated. Findings become tasks. ReadyComply is not the evaluator of record.
Where ReadyComply stops
There is no pass/fail determination for a safeguard in the product. Status is a human field, set by the person who owns it. Connectors, when they exist, file dated evidence against a safeguard. They do not clear it, and they are not the periodic evaluation the Security Rule requires. An OCR investigation, if one ever happens, is not decided by this workspace.
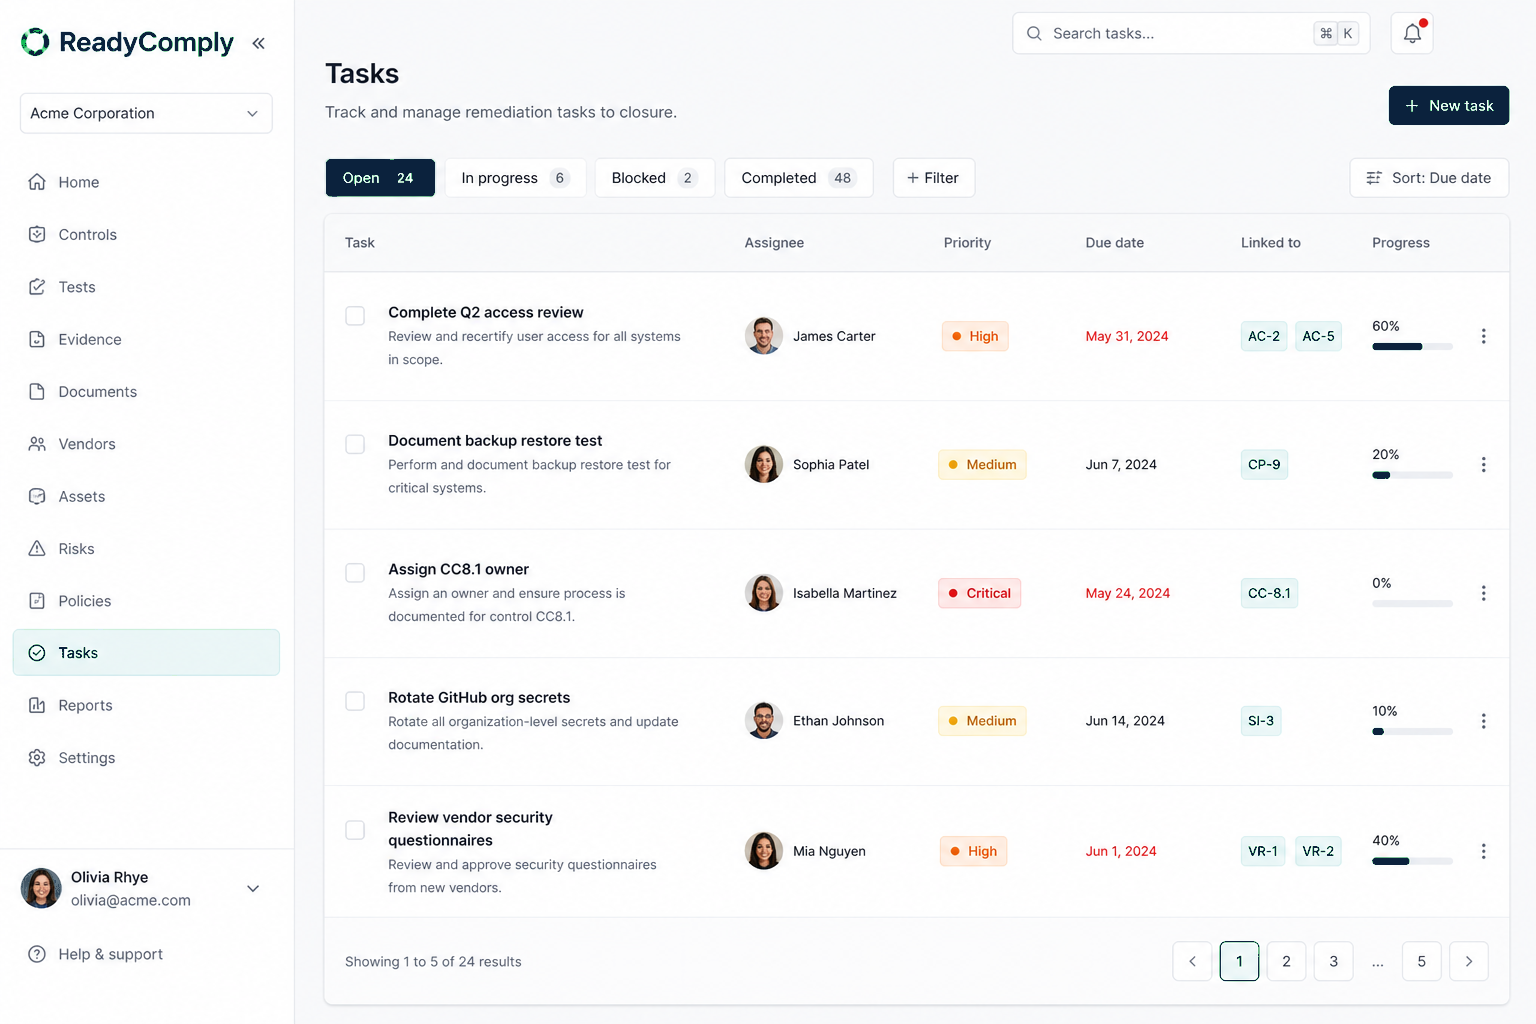
Framework
Workspace
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Checklist
Sign in. Create the first system. Start with what you can already prove.
Sign in