ISMS clauses
Context, leadership, planning, support, operation, performance, improvement — each as a control you can own.
Frameworks · ISO 27001
ISO/IEC 27001 is a management system standard. A certification body audits it. ReadyComply instantiates the clauses and Annex A themes so the audit is not a scavenger hunt. It does not issue the certificate.
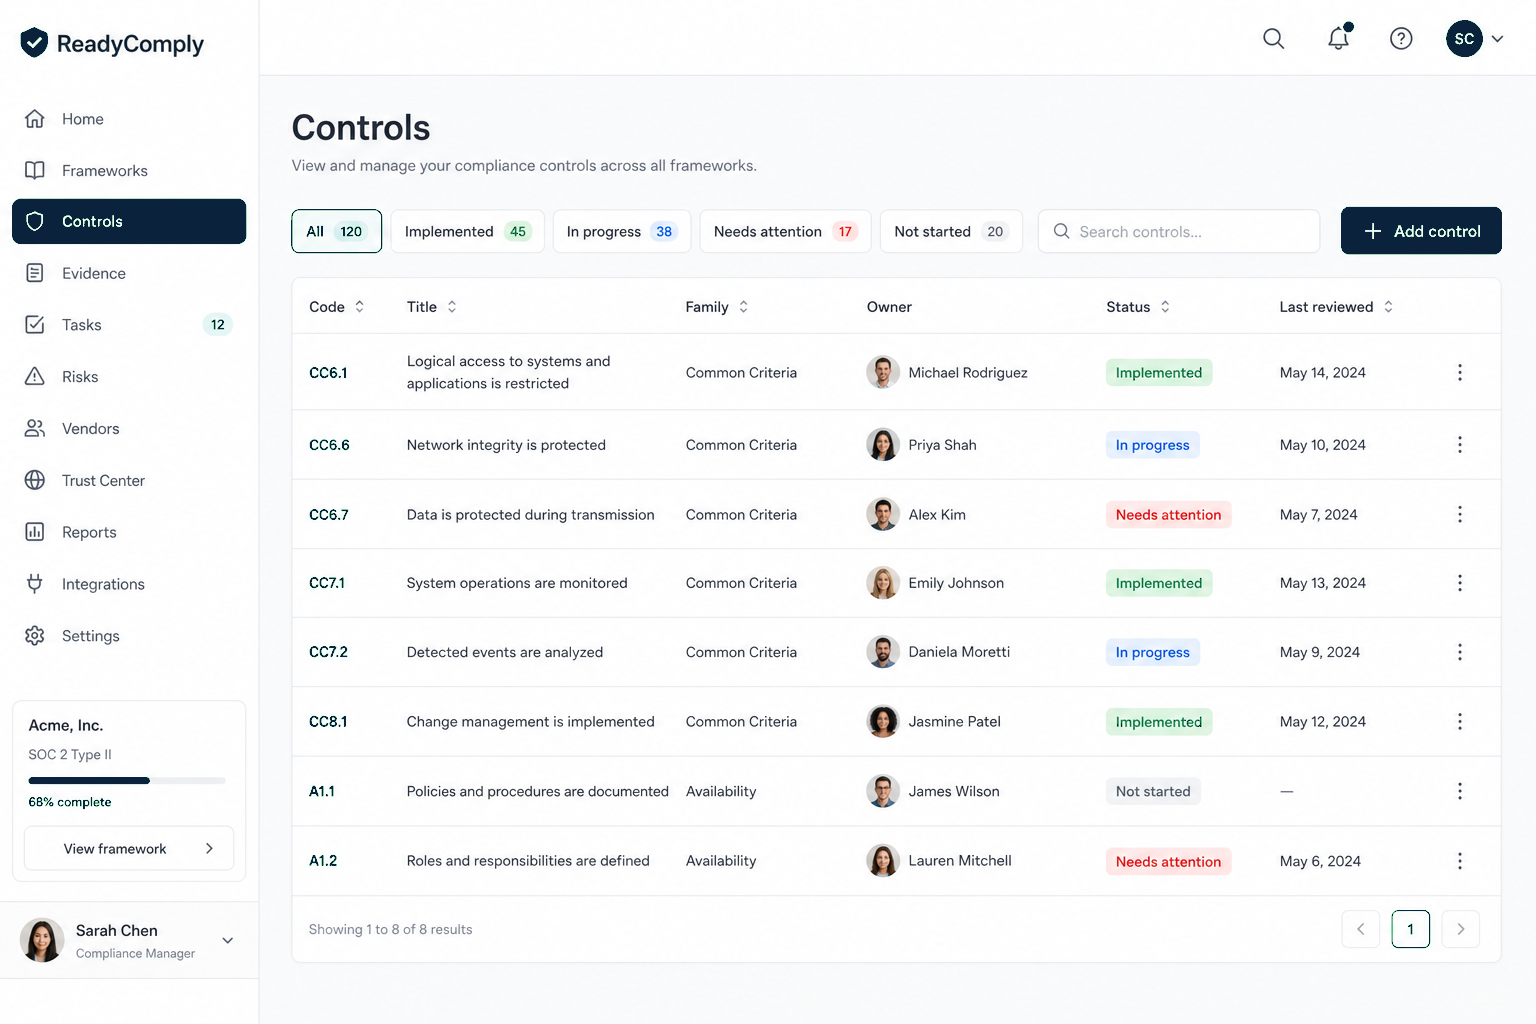
What ISO 27001 is
You define scope, leadership, risk, support, operation, evaluation, and improvement. Annex A.5–A.8 are organizational, people, physical, and technological themes you apply where they fit. Software cannot skip the certification body.
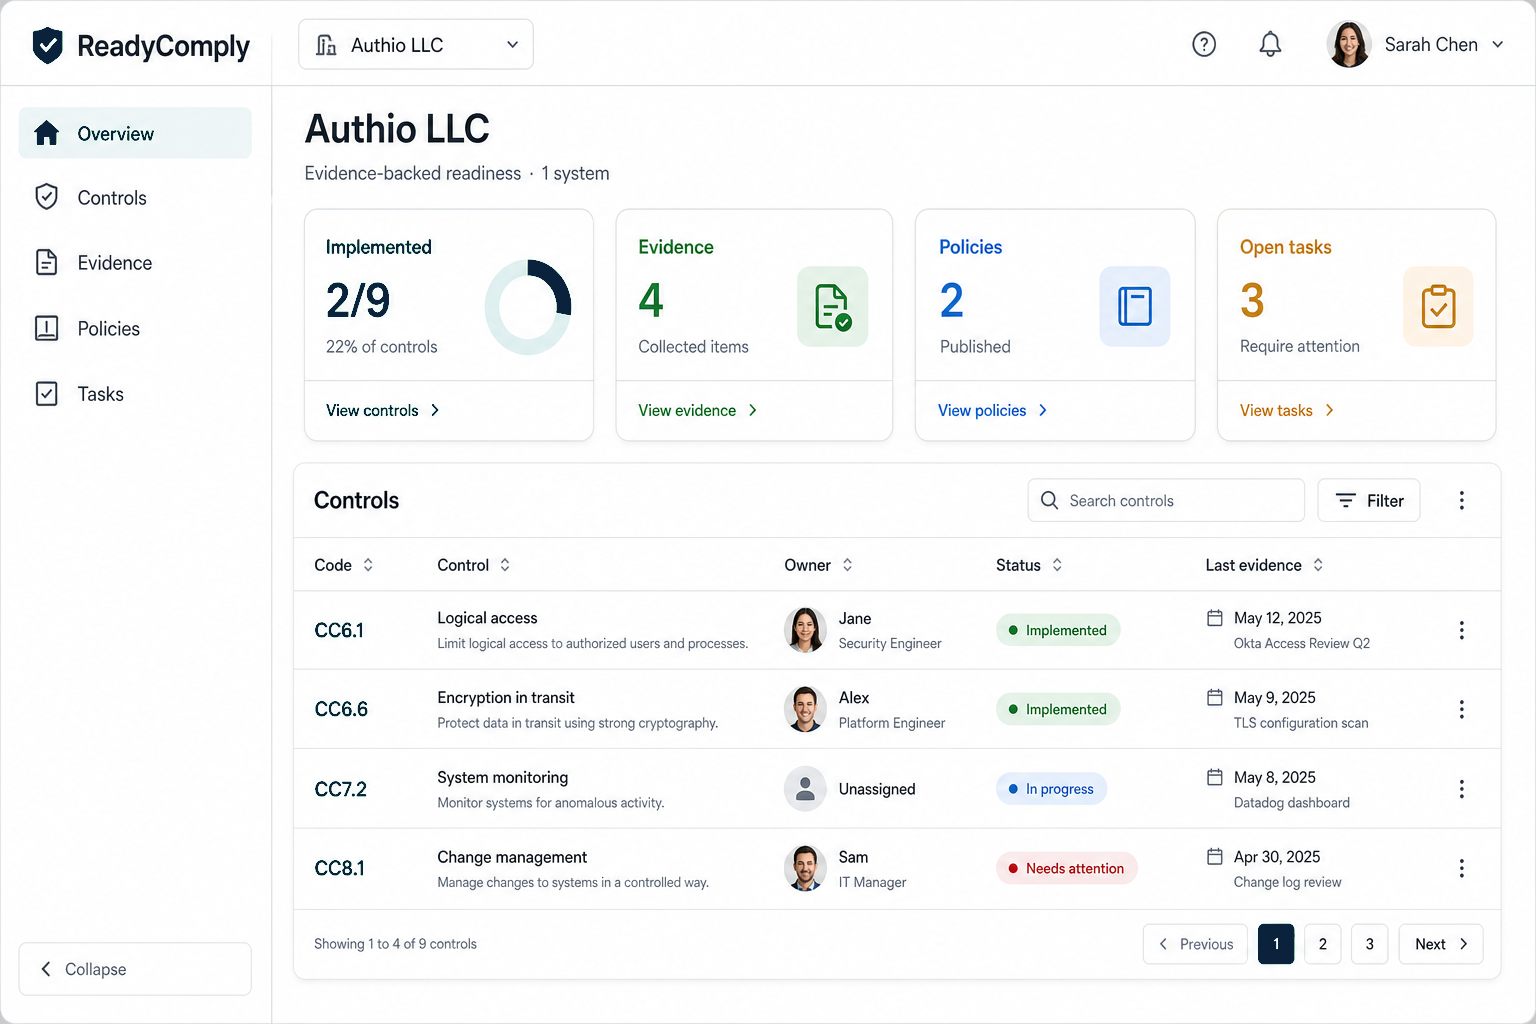
In the workspace
Context, leadership, planning, support, operation, performance, improvement — each as a control you can own.
Four 2022 themes, not ninety-three copied line items. Instantiate what you will evidence.
Cloud-only teams still have to say what the provider covers and keep that attestation on file.
We do not pick a body, sit the audit, or print a mark. Bring your own.
The cycle
Legal entity, systems, locations, and suppliers in. Everything else is a reason.
Version the information security policy next to the clause.
Planning is a control with owners, not a slide.
Mark the rest not applicable with a rationale.
ReadyComply is not UKAS, ANAB, or any other body.
Also in the catalog
Also in ReadyComply
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Read
Sign in. The ISO families instantiate with the system. Fill them in before you buy a stage-1 date.
Sign in