Scope the system
Legal entity, products, infra, and vendors that are in. Everything else is a reason for not applicable.
Resources · SOC 2 guide
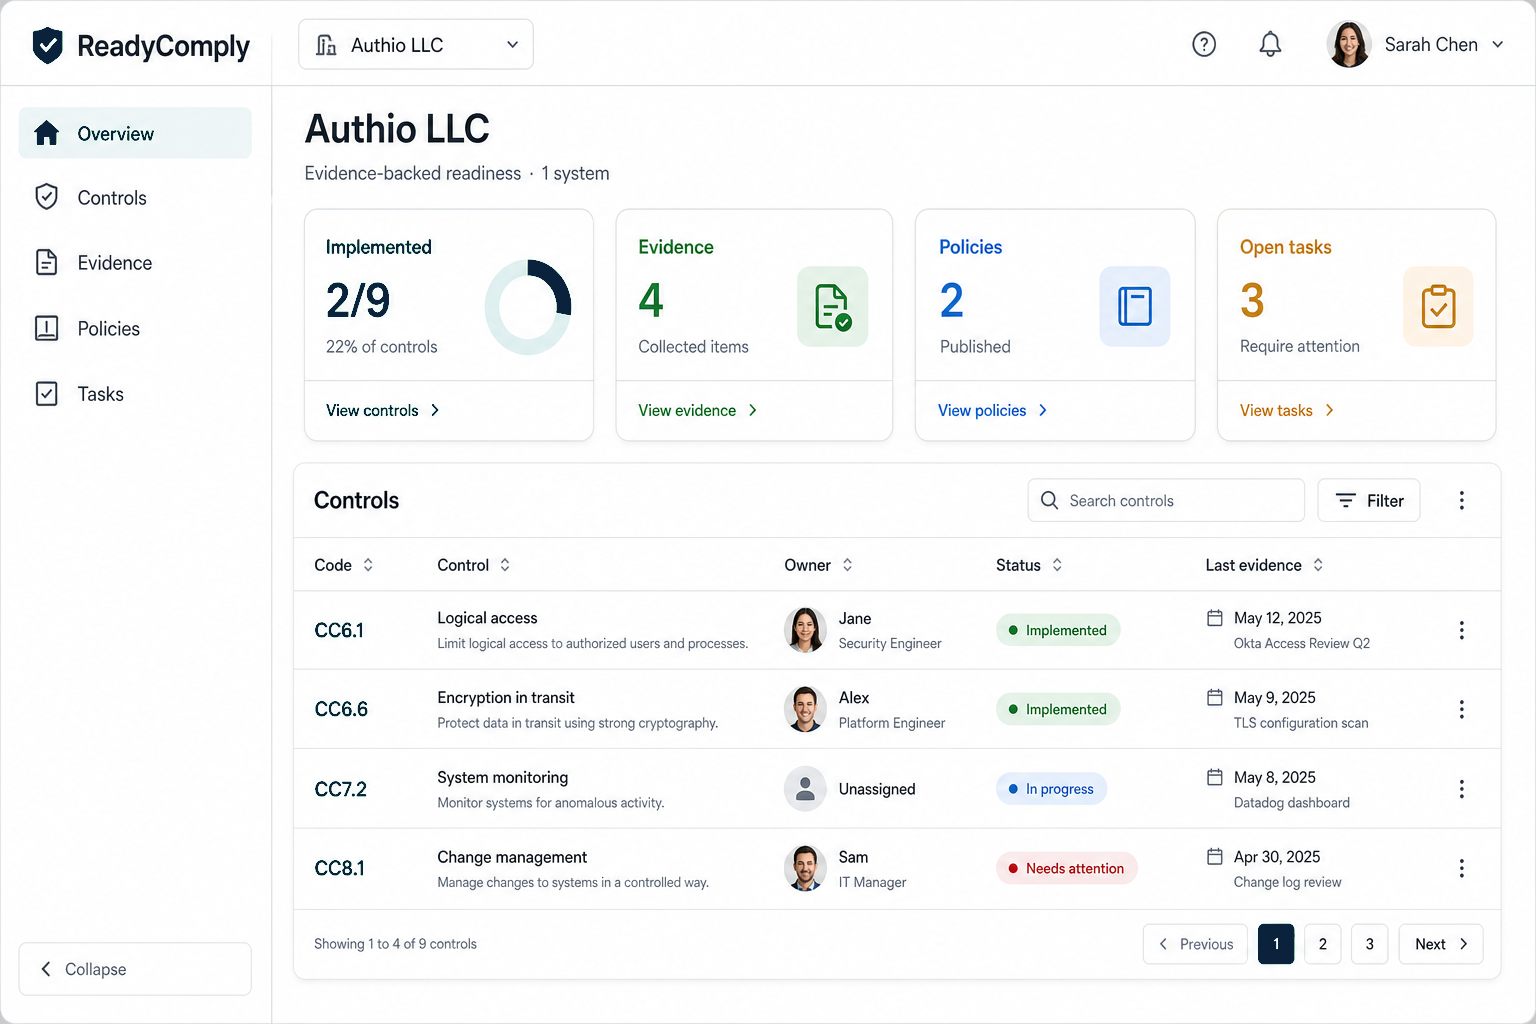
SOC 2 is not a badge you buy from a SaaS product. It is an independent examination. ReadyComply exists so the examination is not a scavenger hunt.
The distinction
A licensed CPA firm examines controls over a period (Type II) or at a point in time (Type I) and issues a report. ReadyComply can hold the criteria, the evidence, the policies, and the gaps. It cannot sign the opinion.
The work
Legal entity, products, infra, and vendors that are in. Everything else is a reason for not applicable.
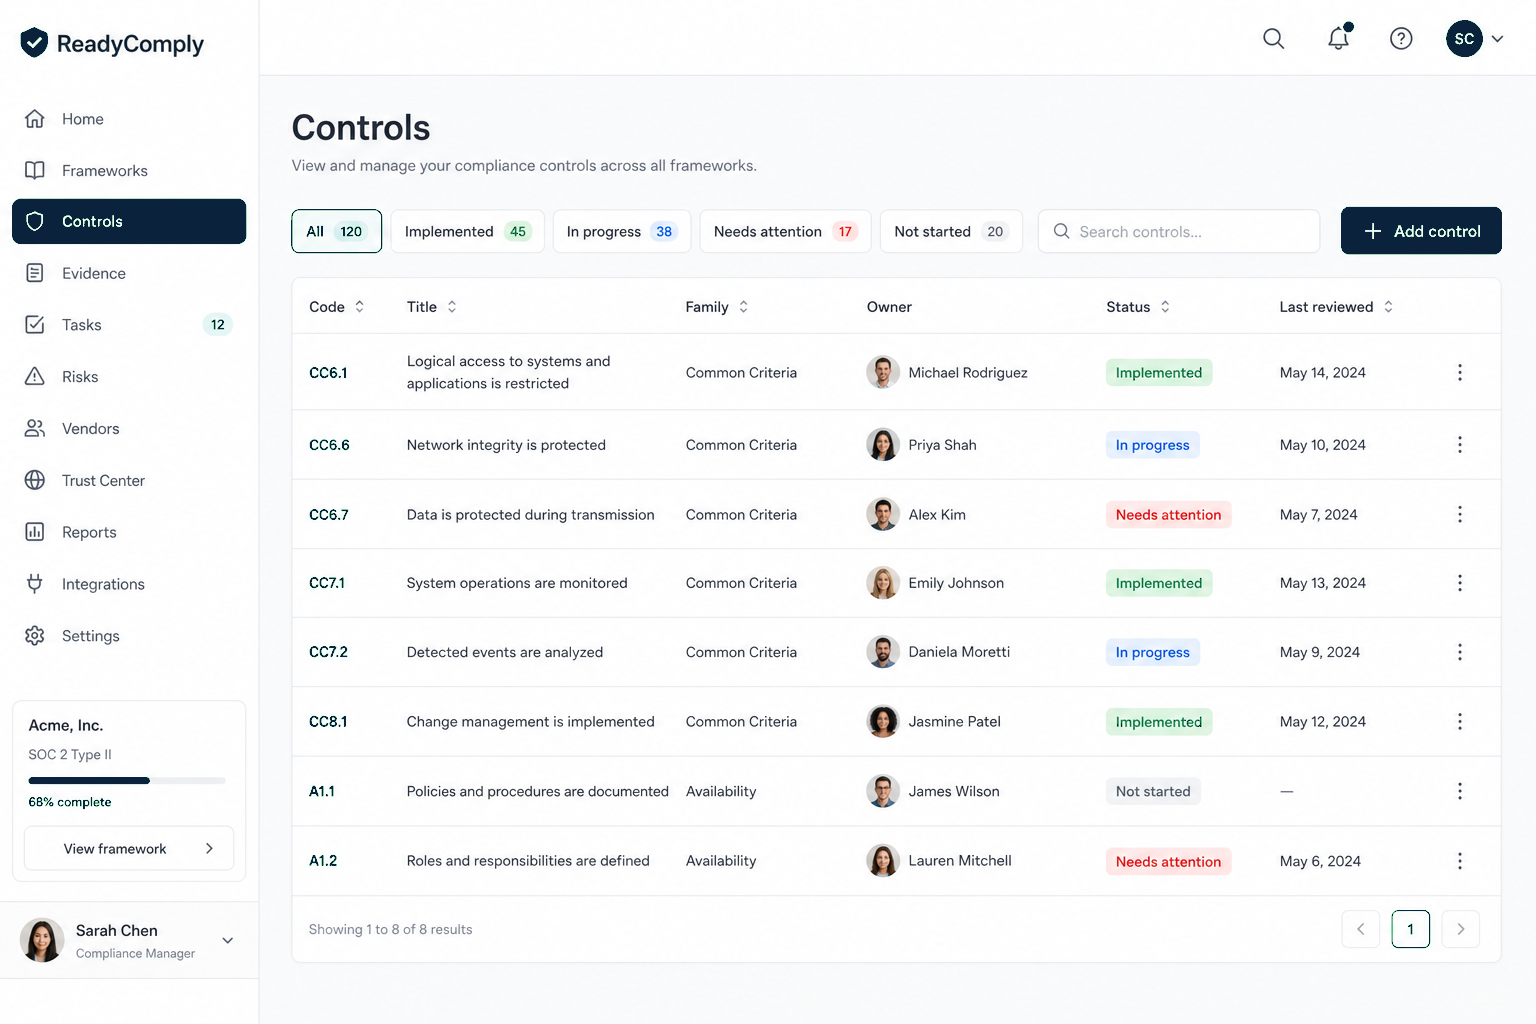
Security at minimum. The rest only if you will evidence them.
Not the AICPA text. Your implementation, your owner, your exceptions.
Artifacts with dates. Tasks with owners. A trail of who changed what.
Where ReadyComply stops
There is no passing grade in the product. Status is a human field. Connectors, when they exist, attach evidence. They do not close the opinion. If a page on this site sounds like a certificate, it is wrong.
Framework
Workspace
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
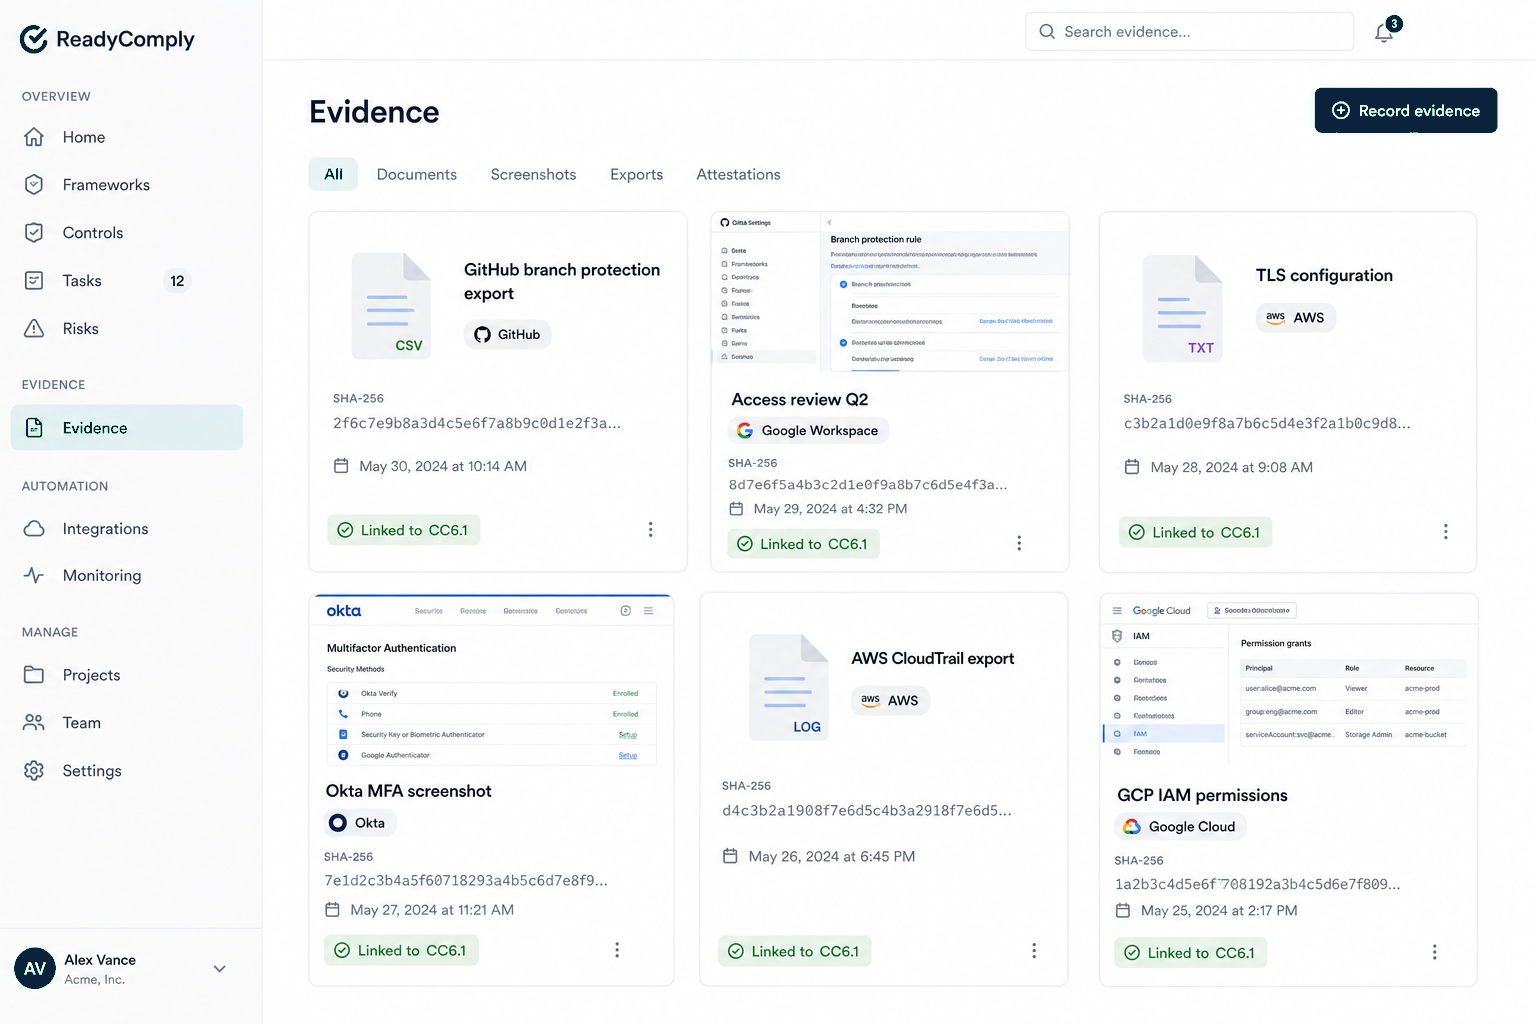
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Sign in. Create the first system. Start with what you can already prove.
Sign in