Purposes and bases
Every processing purpose named, with a lawful basis that is not a guess.
Resources · GDPR guide
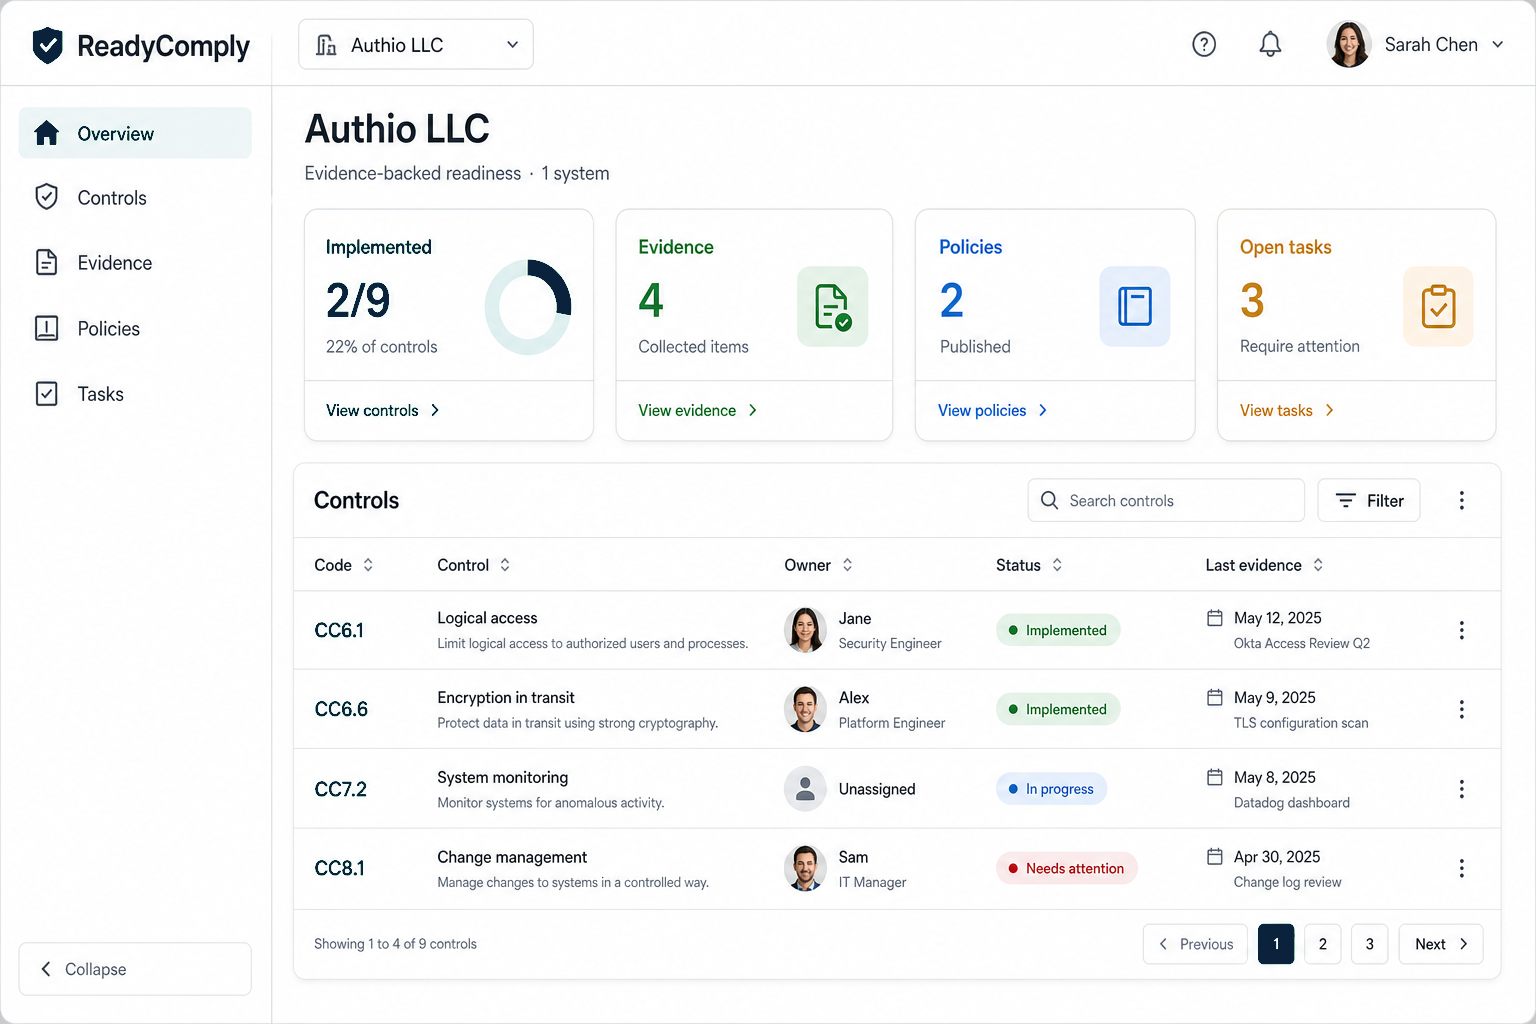
GDPR is enforced by supervisory authorities, not by a compliance product. ReadyComply holds purposes, records, rights, processors, and transfers. It does not decide you are adequate.
The distinction
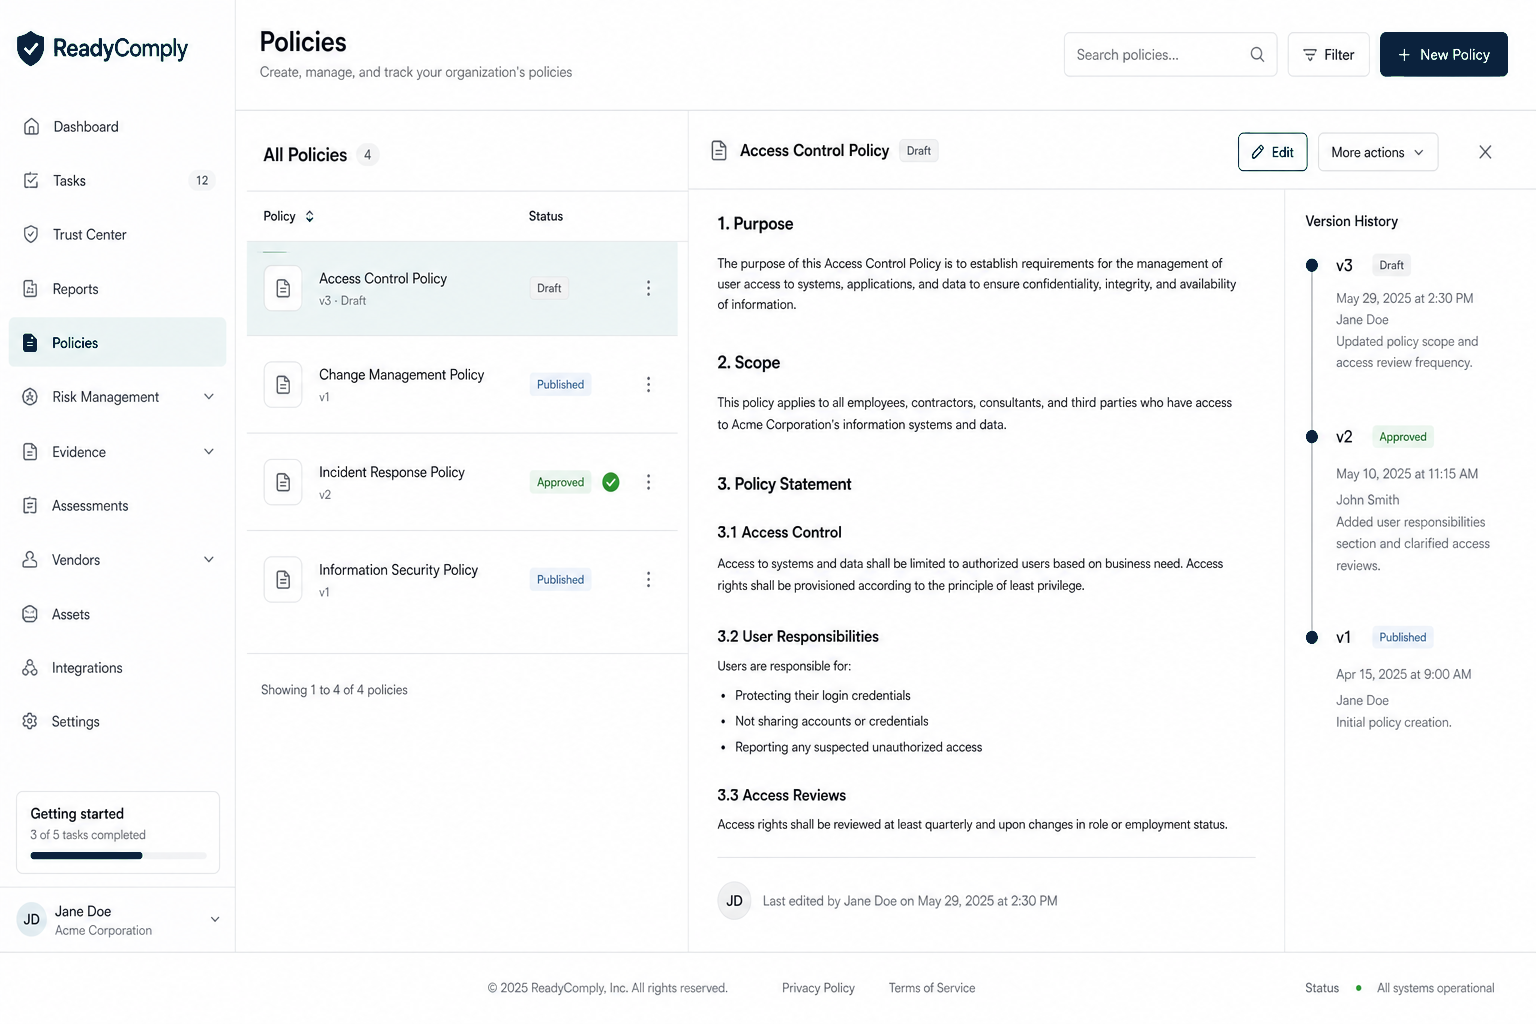
Article 30 records are a living inventory of processing. A marketing page that says “we care about privacy” is not that inventory. Version the notice. Keep the RoPA in evidence with a date.
The work
Every processing purpose named, with a lawful basis that is not a guess.
Access, erasure, portability, and the rest need an owner and an SLA, not a mailto link.
DPAs and a transfer mechanism. Subprocessors should match the list you publish.
Article 32 should not contradict your SOC 2 or ISO technical story.
Where ReadyComply stops
There is no compliance score for an article in the product. Status is a human field. Connectors, when they exist, attach evidence to a record or a processing entry. They do not rule on lawful basis, and they do not stand in for your DPO, your counsel, or a supervisory authority. If a page on this site sounds like a certification, it is wrong.
Framework
Workspace
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
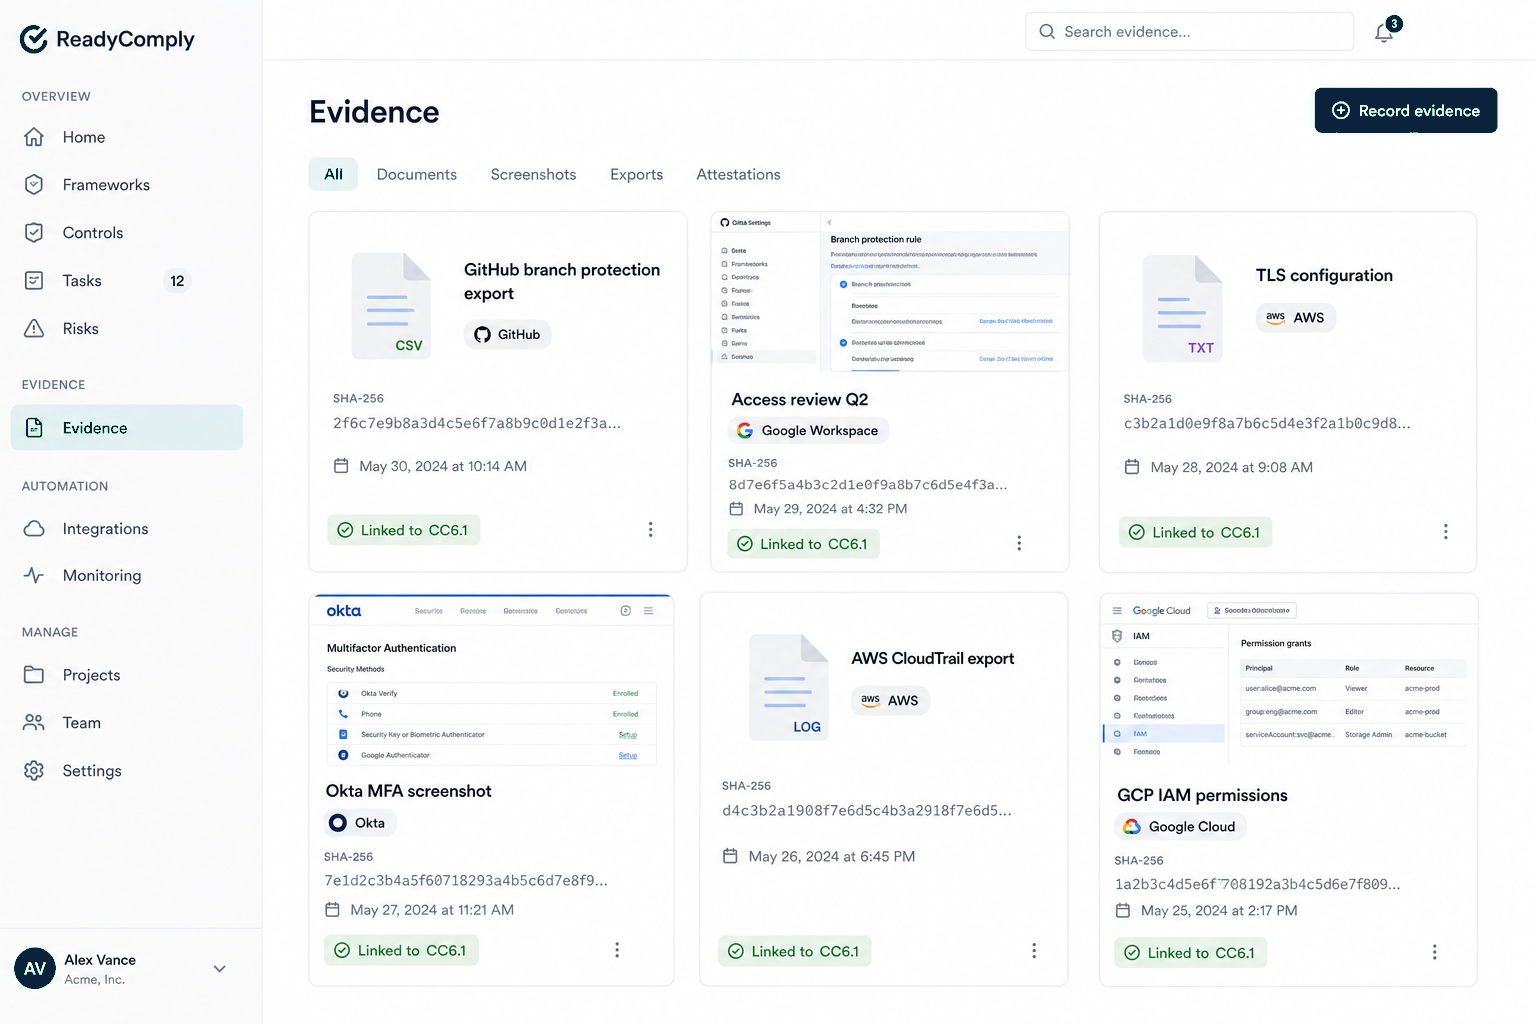
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Checklist
Sign in. Create the first system. Start with what you can already prove.
Sign in