Resources · GDPR checklist
Accountability, in order. Mapped to the workspace.
Checking a box here does not mean a supervisory authority agrees. It means the register has the record they will ask for.
Purposes
Before you collect another field.
- 01
Each processing purpose is named.
If you cannot name it, do not collect it.
- 02
Each purpose has a lawful basis.
Consent is not the default for a SaaS control plane.
- 03
Privacy notice is versioned and live.
File the URL as evidence against transparency.
Accountability
Inside ReadyComply.
- 01
RoPA is dated.
Article 30 is a living record, not a one-off spreadsheet.
- 02
Rights path has an owner and an SLA.
Access, erasure, portability, objection — who authenticates, who fulfils.
- 03
Processors have DPAs.
The list should match what you publish.
- 04
Transfers have a mechanism.
Adequacy, SCCs, or a real exception. File the signed SCCs.
- 05
Article 32 agrees with SOC 2 and ISO.
Do not keep three conflicting security stories.
Incidents
When it goes wrong.
- 01
Breach tabletop has a date.
Who decides on 72-hour notification. ReadyComply is not the authority.
- 02
Processor breach terms are in the DPA, not assumed.
How fast a processor tells you matters more than how fast you tell the authority, since your clock starts on their notice.
- 03
The data-subject notification threshold is written down in advance.
“High risk” is a judgment call. Make it before an incident, not during one.
Also in ReadyComply
Open the modules.
Controls
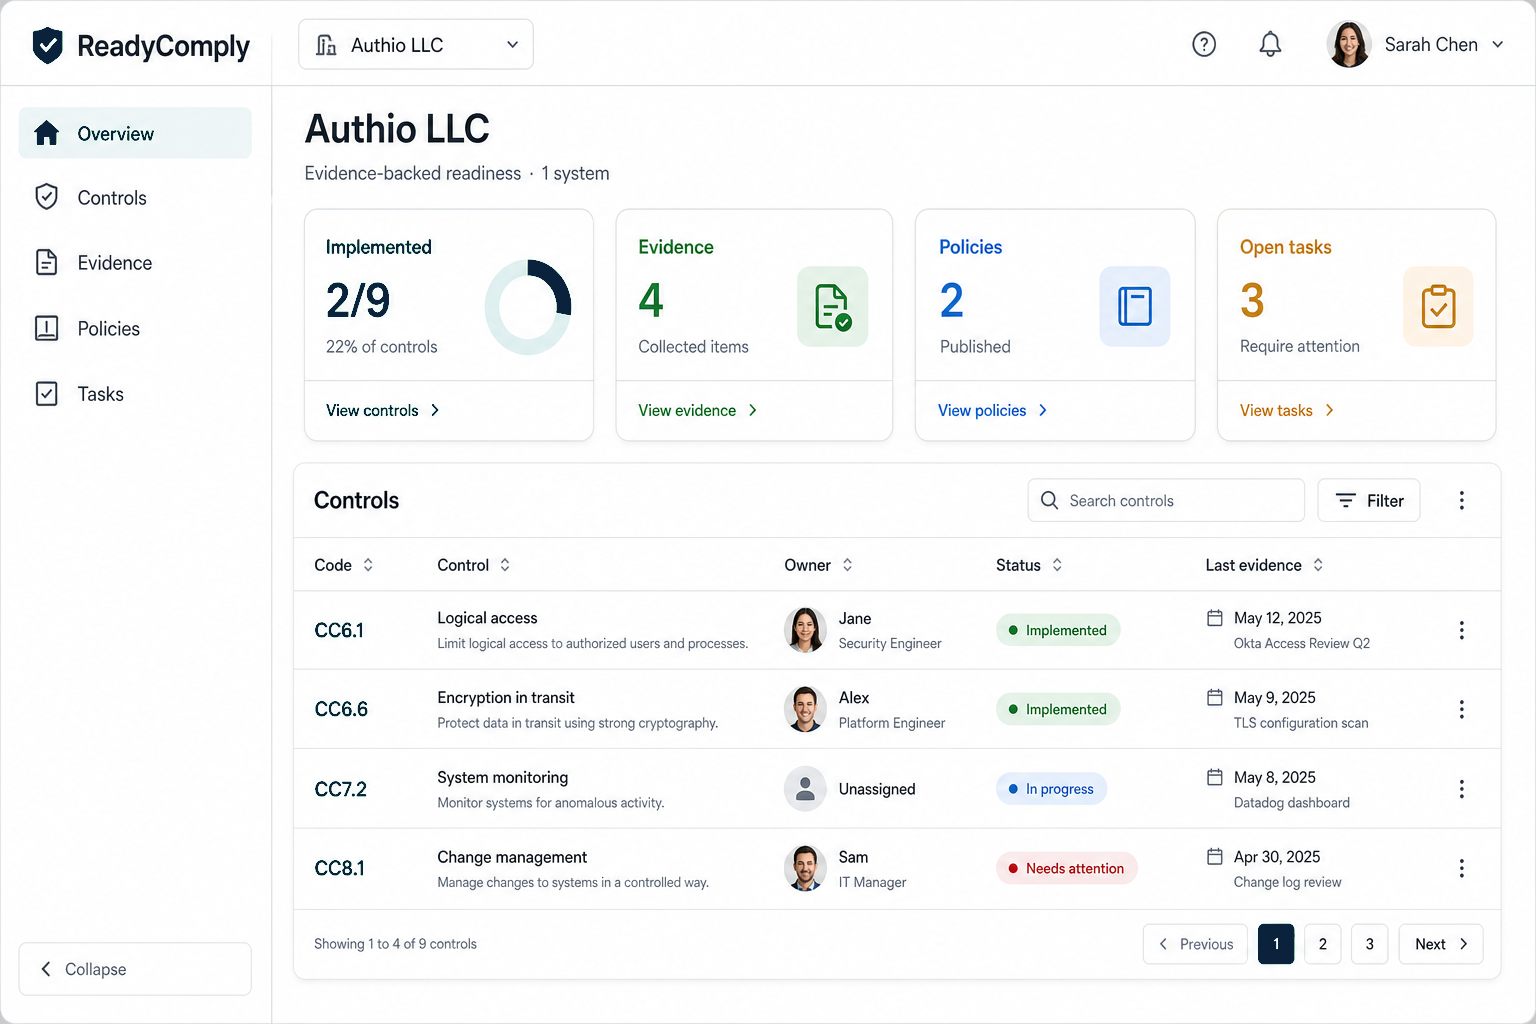
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
Evidence
File what you have against a control. Manual upload or a read-only connector.
Policies
Versioned drafts next to the controls they support. Know which text is current.
Frameworks
All four catalogs.
SOC 2
Trust Services Criteria as a readiness register. The report is still a CPA firm.
ISO 27001
ISMS clauses and Annex A themes. Certification is a body, not this product.
HIPAA
Security Rule safeguard families. A BAA and an OCR review are still yours.
GDPR
Accountability articles for a SaaS register. Not a supervisory-authority opinion.
Guide
Read the longer page.
Open the workspace. Keep the register current.
Sign in. Create the first system. Start with what you can already prove.
Sign in