Security
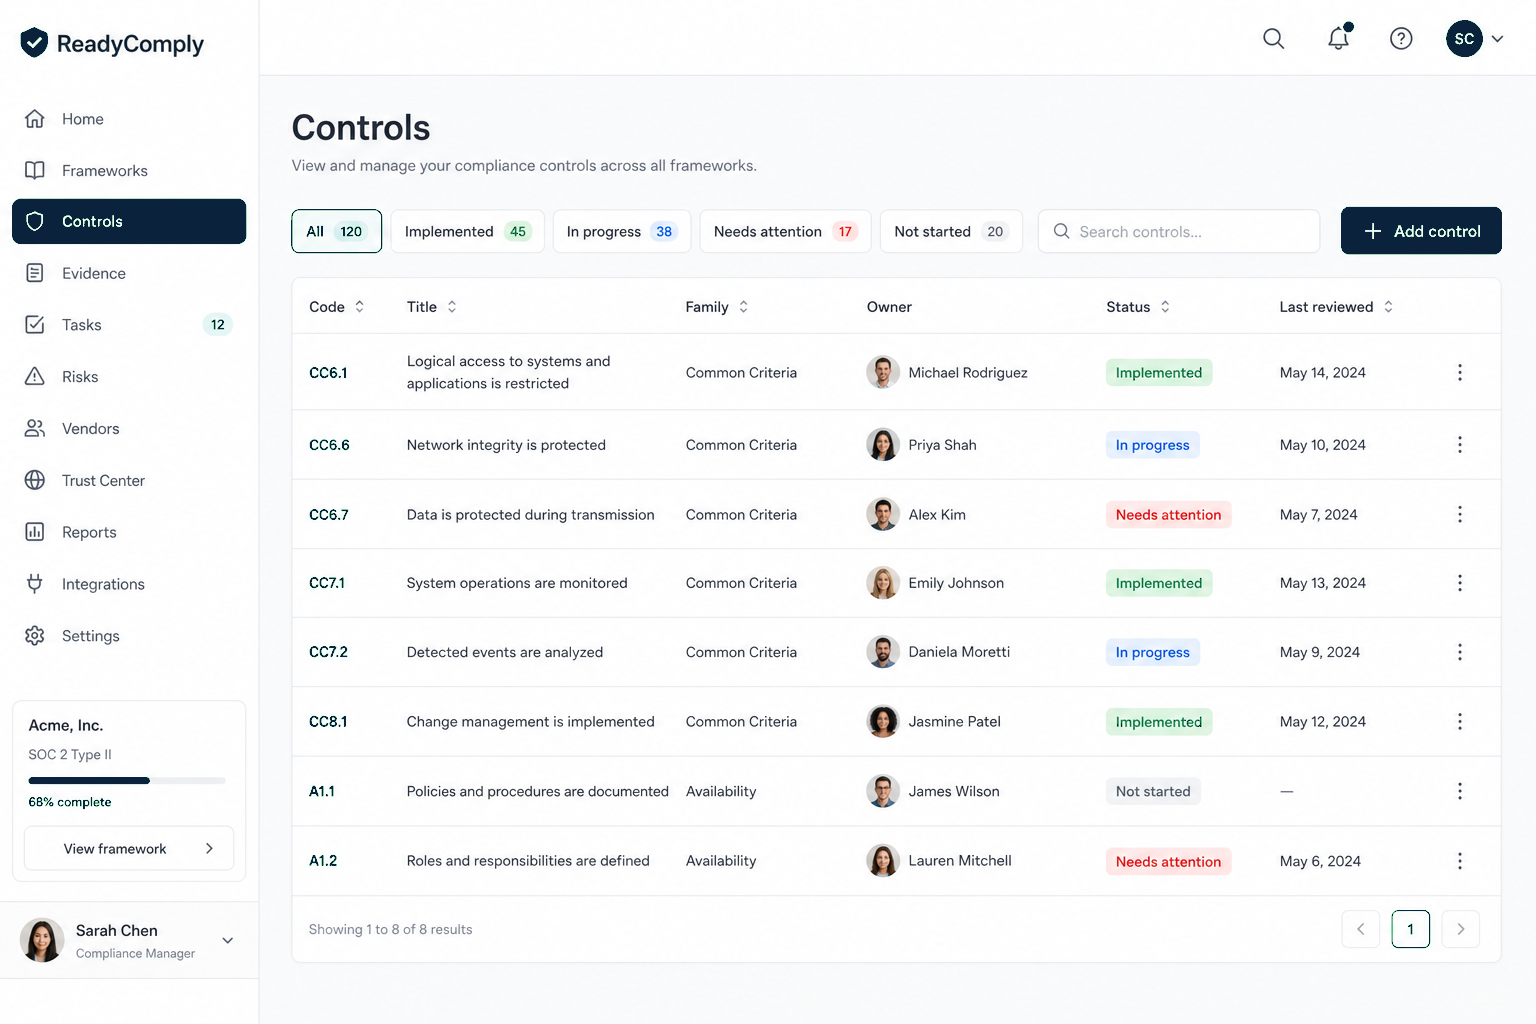
The starter family ReadyComply instantiates per system. Access, change, and operations you can actually show.
Frameworks · SOC 2
SOC 2 is an independent examination by a licensed CPA. ReadyComply is the register you keep so that examination is not a scavenger hunt. It does not issue the report.
What SOC 2 is
A Type I report describes controls at a date. A Type II report tests them over a window. Software cannot skip that. A platform can only keep the criteria, evidence, policies, and gaps in one place while you run the period.
Trust Services Criteria
The starter family ReadyComply instantiates per system. Access, change, and operations you can actually show.
In scope only if you claim them. Do not instantiate a criterion you will not evidence.
The report is about a system, not a logo. Name the products, infra, and vendors that are in.
Out of scope needs a reason. Empty is not a reason.
The cycle
Legal name, Authio organization, system boundary.
Assign owners. Write how each control operates here.
Date it. Hash it if you can. Link it to the control.
Owner, due date, trail. Close them in the register.
ReadyComply is not the firm and does not pick one for you.
In the workspace
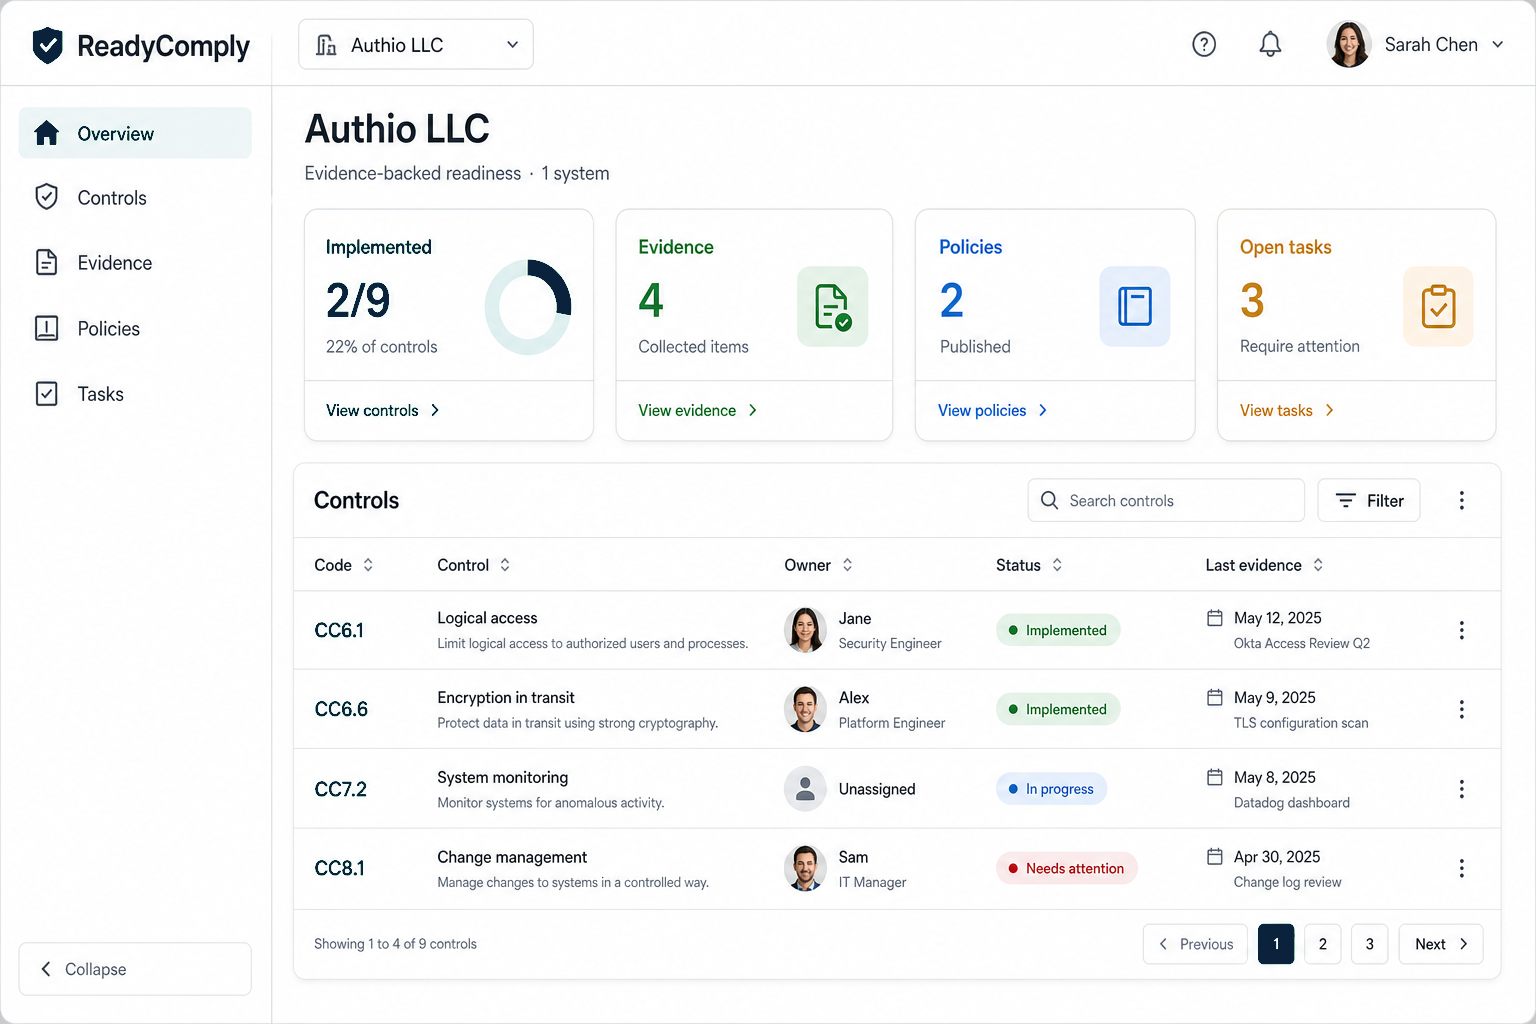
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Also in the catalog
Sign in. Name the first system. Instantiate Security. That is the beginning of a SOC 2, not the end of one.
Sign in