Principles and lawfulness
Purposes and a real lawful basis. Consent is not the default for a control plane.
Frameworks · GDPR
GDPR is a regulation. Supervisory authorities enforce it. ReadyComply instantiates the articles a SaaS team actually has to operate: purposes, rights, processors, security, breaches, transfers. It does not issue an adequacy decision.
What GDPR is
Lawful, fair, transparent, purpose-limited, minimized, accurate, storage-limited, secure, and accountable. If you cannot show the purpose for a field, you should not keep the field. The register is where that argument lives.
In the workspace
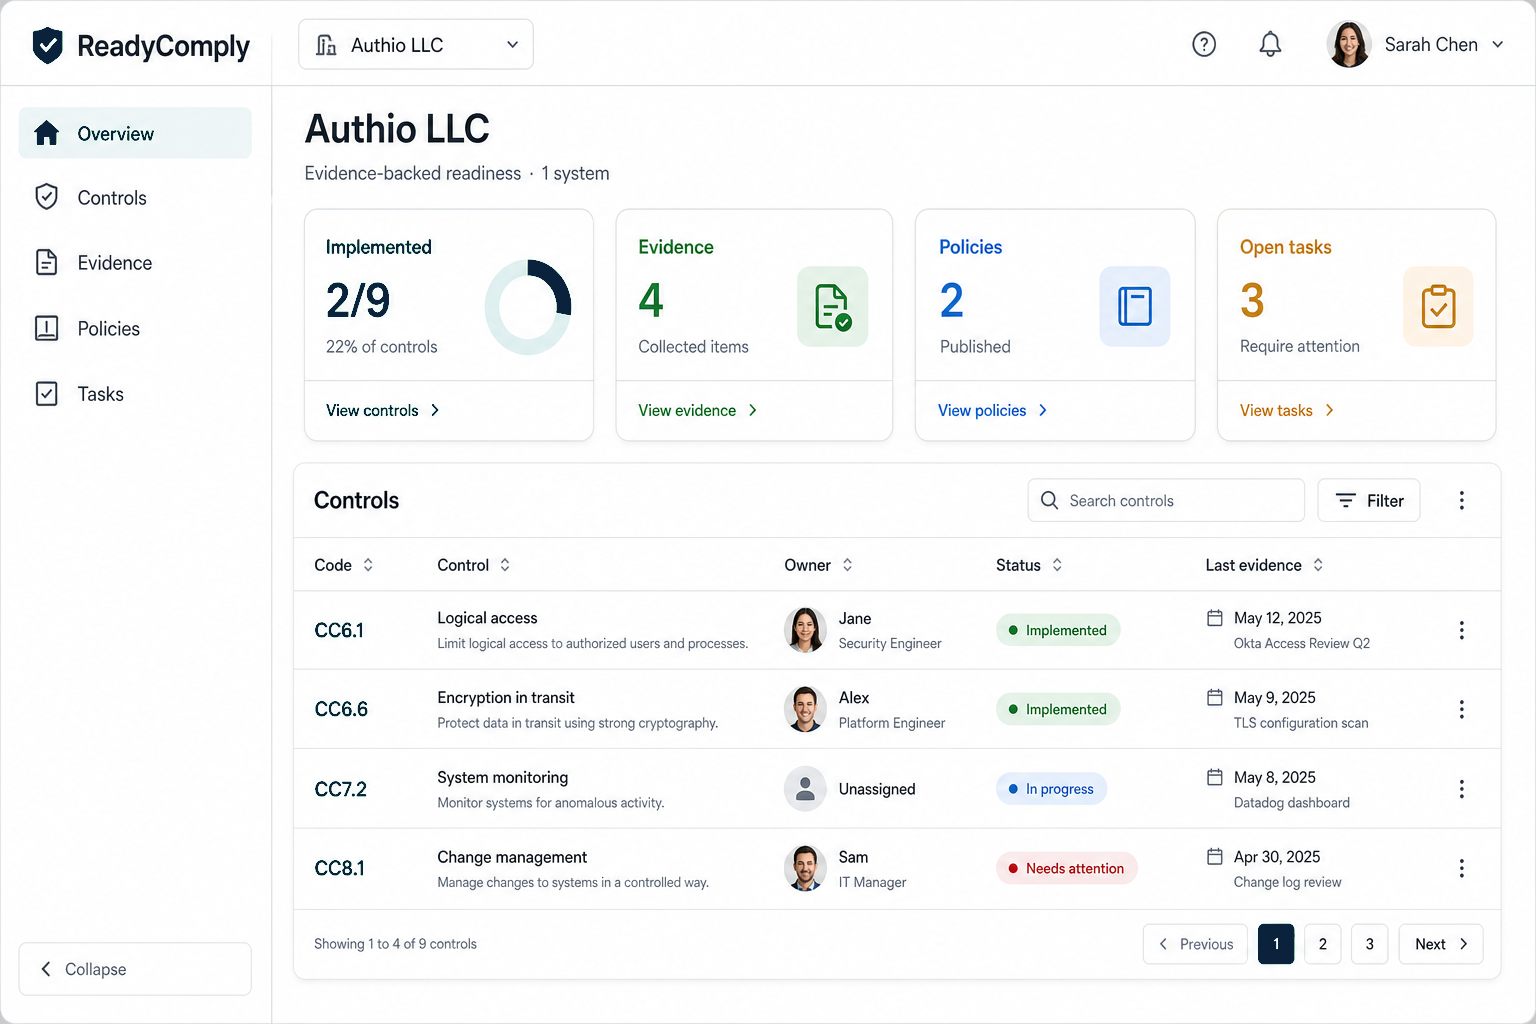
Purposes and a real lawful basis. Consent is not the default for a control plane.
A versioned notice, and a path to access, erasure, portability, and the rest.
A dated RoPA and DPAs with anyone who processes for you.
Article 32 should agree with your SOC 2 and ISO technical story. Transfers need a mechanism, not a hope.
The cycle
Each processing purpose on the system, with a basis.
Version it in policies. File the live URL.
Who authenticates the requester, who fulfils, how long.
Contracts and SCCs in evidence, dated.
ReadyComply is not your supervisory authority and does not certify you.
Also in the catalog
Also in ReadyComply
Scope SOC 2, ISO 27001, HIPAA, and GDPR families to each system. Track status, owner, and why something is out of scope.
File what you have against a control. Manual upload or a read-only connector.
Versioned drafts next to the controls they support. Know which text is current.
Read
Sign in. GDPR families instantiate with the system. Fill the RoPA in.
Sign in